One size does not fit all

One Size Fits No One.

Risk never sits in one place. It concentrates in a small group of employees, shifts with the threats targeting your industry, and moves faster than an annual training calendar. Training that treats every employee the same can't keep up with it.

Running the program isn't the same as reducing the risk.

Employees can tell when training wasn't built for them.

Stale, templated phishing simulations get spotted immediately, and the lesson people take away is how to recognize the test, not the attack. Real phishing, increasingly AI-generated, looks nothing like a static template library.

A security awareness library that reads the same at every company is easy to write off as compliance theater. Once employees tune it out, it stops doing its job.

Screenshot of an email inbox with a targeted phishing simulation, customized according to the recipient’s role, training progress, and geographic location.

"Everyone finished the training" isn't an answer.

Modules get deployed, completion stays high, and the quarterly deck looks tidy. None of that shows whether employees are harder to trick than they were six months ago.

When a board or a cyber insurer asks what's actually changing, completion and fail rates don't hold up. They show activity, not a reduction in risk.

Side-by-side view of the Hoxhunt admin interface for managing security training and the end-user interface showing a finalized training module.

A single module can't cover uneven risk.

Most programs deploy the same training to everyone and measure success by who finished it. That works if risk is spread evenly across the organization. It isn't.

At Qualcomm, 4% of employees accounted for 80% of phishing incidents. A module built for the average employee under-trains the people driving most of the exposure and over-trains everyone else.

Side-by-side view of a user being informed of a reported email’s threat level and the corresponding incident automatically logged in the admin dashboard.

Training built around where risk actually concentrates.
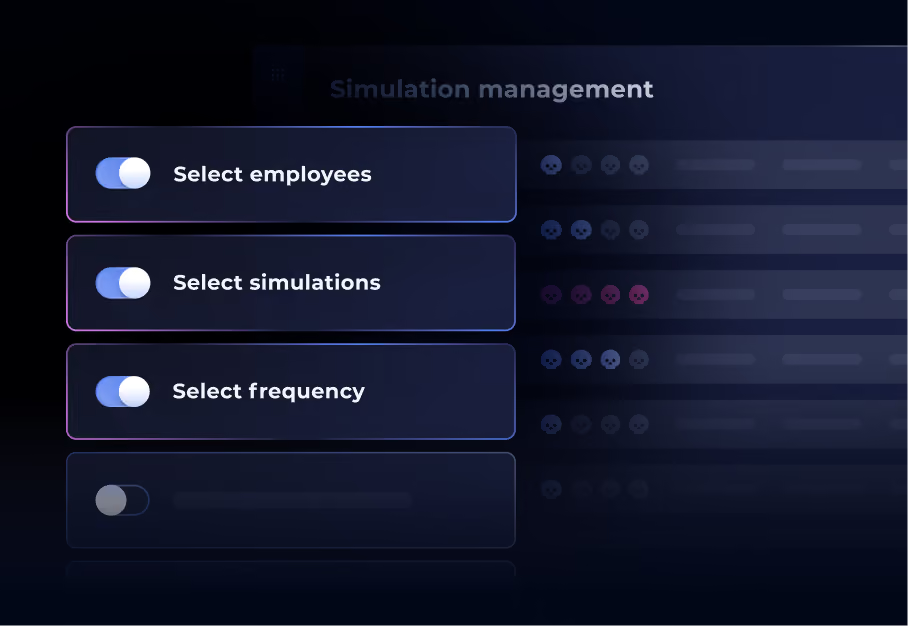
Hoxhunt pairs Adaptive Phishing Training with security awareness training built for each organization, not assembled from a shared template library. The skill algorithm keeps every employee in a zone where they're challenged but able to succeed. Four things make that possible:
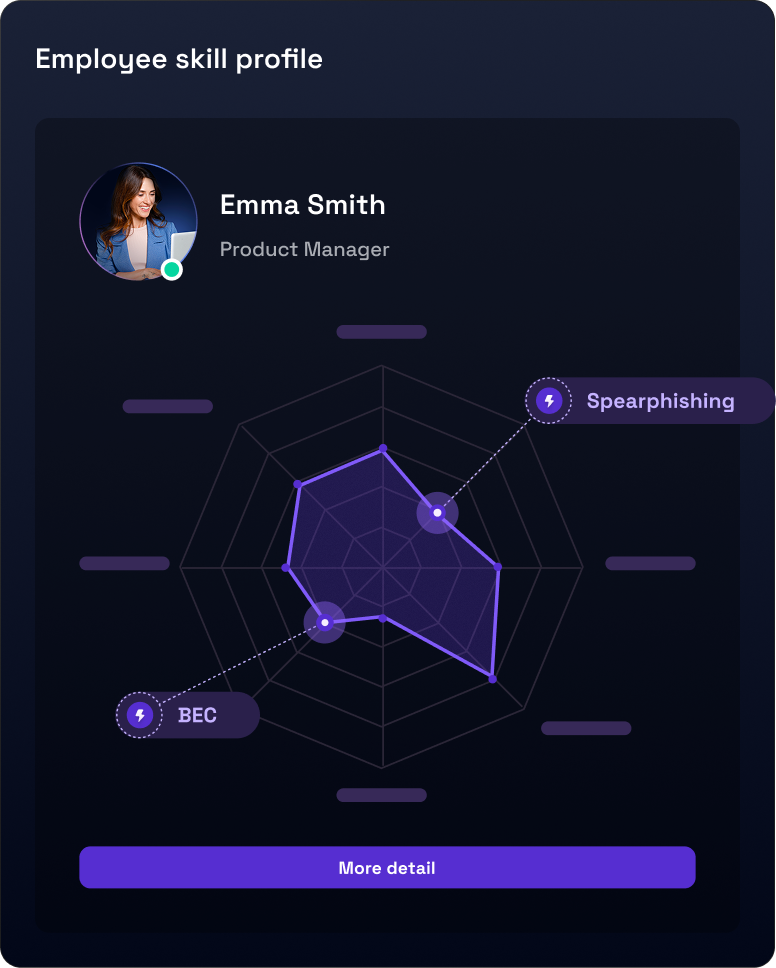
UI view with Hoxhunt's Human Risk Score highlighted

The riskiest employees get the most practice.

Risk concentrates in a small group, so training effort should too. For Change-license customers, Hoxhunt automatically increases simulation frequency for employees who click too often, until they report one or stop failing.
Gap between simulations shortens by about 50% for repeat clickers
Cadence returns to normal once behavior improves
No manual cohort-building or targeting
Qualcomm's riskiest 1,000 went from double their peers' failure rate to roughly half in nine months, winning a CSO50 Award
UI view with Hoxhunt's Human Risk Score highlighted

Simulations follow the threats, not a template library.

Attacks shift by industry and region, and a static template library can't account for that. When enabled, Hoxhunt biases simulations toward what's actually trending for your organization.
Weighted toward threats trending in your industry or region
Built from your own reported threats with Threat Upload
Employees train on what's actually reaching inboxes
UI view with Hoxhunt's Human Risk Score highlighted

Training that reflects your rules, not everyone's.
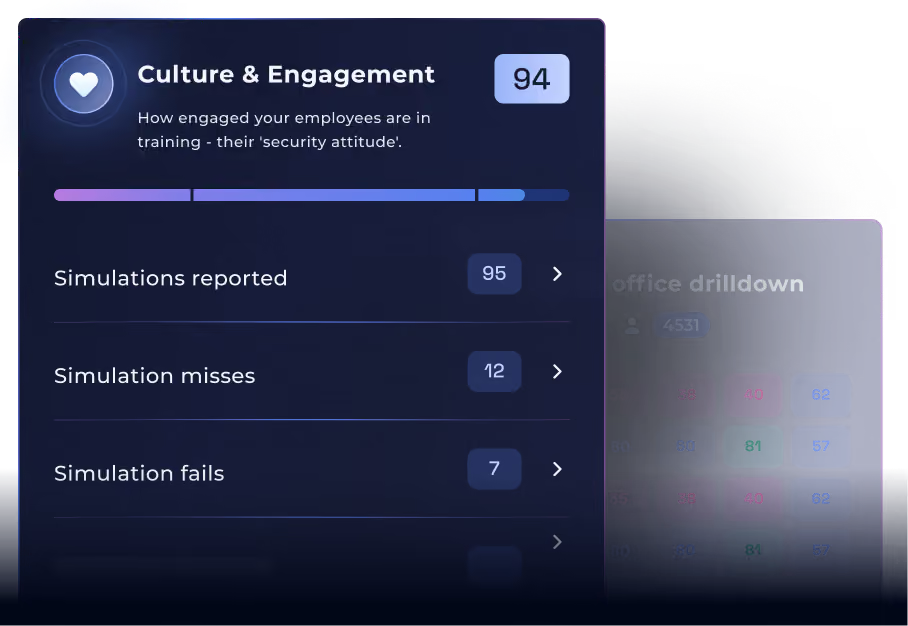
Security awareness training doesn't have to run on the same generic modules as every other company's program. Admins generate content from their own policies and industry, then review it before it goes live.
Generated from your policies and industry
Drafted in minutes, not a quarter-long content project
Reviewed and approved by admins before launch
UI view with Hoxhunt's Human Risk Score highlighted

A program that scales without a bigger team.

Hoxhunt runs simulations continuously and routes reported real threats into existing security tools automatically, so program size isn't tied to team size.
Continuous delivery, no manual campaign scheduling
Reported threats routed into existing security tools
Runs on behavioral signals instead of manual administration
Uber runs its program for 25,000+ users with a two-person team

Our Reviews Speak for Themselves

AES Logo
CSO50 Awards winner badge
AES engages 5x more employees with Hoxhunt compared to legacy SAT tools
526
%
increase in reporting rate
79
%
decrease in failure rate
Read the full story
Avanade Logo
Avanade saves over 900 hours of SOC analysis per month
259
%
increase in resilience ratio
900
hrs
monthly SOC analyst time saved
Read the full story

Risk isn't one size. See what works for an organization like yours

Learn how Hoxhunt can effortlessly transform your training program and reduce your human cyber-risk.

In 20 minutes, we'll show you where risk actually concentrates in your organization and what changes when training adapts to it.

G2 Top 50 Enterprise Products 2026 - badgeG2 Top 50 Security Products 2026 - badgeGartner Peer Insights Customers' Choice 2024 badgeCapterra Best Ease of Use 2025 badgeSoftware Advice Most Recommended 2025 badge