The short answer
Cybersecurity Awareness Month is the October campaign, launched in 2004 and led today by CISA and the National Cybersecurity Alliance, that gives security teams a month to change employee behavior. The 2026 themes are CISA’s “Securing the Next 250” and the NCA’s “Don’t Make It Easy for Them”; Hoxhunt’s free toolkit packages a four-week campaign, about 15 minutes a week.
Cramming four weeks of phishing emails and quizzes into October for a check-box test does little. The most effective campaigns deliver periodic bursts of engaging, interactive activities like vishing and smishing drills, deepfake challenges, and expert videos.
A campaign month lands better when it plugs into something continuous. If you are building that, start with how to run a security awareness training program and treat October as one burst inside it.
Awareness month sticks the landing when it feeds a year-round effort; think of it as the capstone to the preceding 11 months of security awareness training, and the launching-off point to the next 11 months of human risk management. That’s why it helps to know how to build a human risk management program.
The goal
Stronger reporting behavior that outlasts October.
You can stretch a campaign across all four weeks, but security leaders are increasingly concentrating on one or two week bursts to keep attention high and fatigue low.
Instead of generic cybersecurity awareness training or one-off posters, we’ve seen the best results from outcome-driven activities: omnichannel phishing simulations (email, smishing, Microsoft Teams, QR), quick microlearning, and visible leadership kickoffs. These sharpen detection skills, boost reporting rates, and link October back to your year-round cybersecurity awareness program.
Below you’ll find 10 proven Cybersecurity Awareness Month ideas, a week-by-week plan, the free official resources, and the metrics that prove the campaign changed behavior. You can put all of it into practice with the free Hoxhunt Cybersecurity Awareness Month Toolkit, built around Hoxhunt’s own campaign line, “Cybersecurity is a team sport,” which Caitlin “Cybersecurity Girl” Sarian explains in the video below.
Hot off the big stages and bright lights at Davos, the NATO Summit, RSA, Black Hat, and pretty much every major cyber event, Caitlin “Cybersecurity Girl” Sarian joins Hoxhunt to promote the 2026 Cybersecurity Awareness Month Toolkit. Because this Cybersecurity Woman of the Year and Hoxhunt truly believe that cybersecurity is a team sport!
“Cyber and athletics are the same. Knowing the rules gets you warmed up, but you win by actually doing the work: Again, and again, and again. The daily phishing emails, the shady text messages, the fake phone calls. To be ready for anything, you have to build your cyber skills before the match begins. In this sport, your coach is your security team... and your teammates are your coworkers. And every time you hit report, you protect the whole squad.”
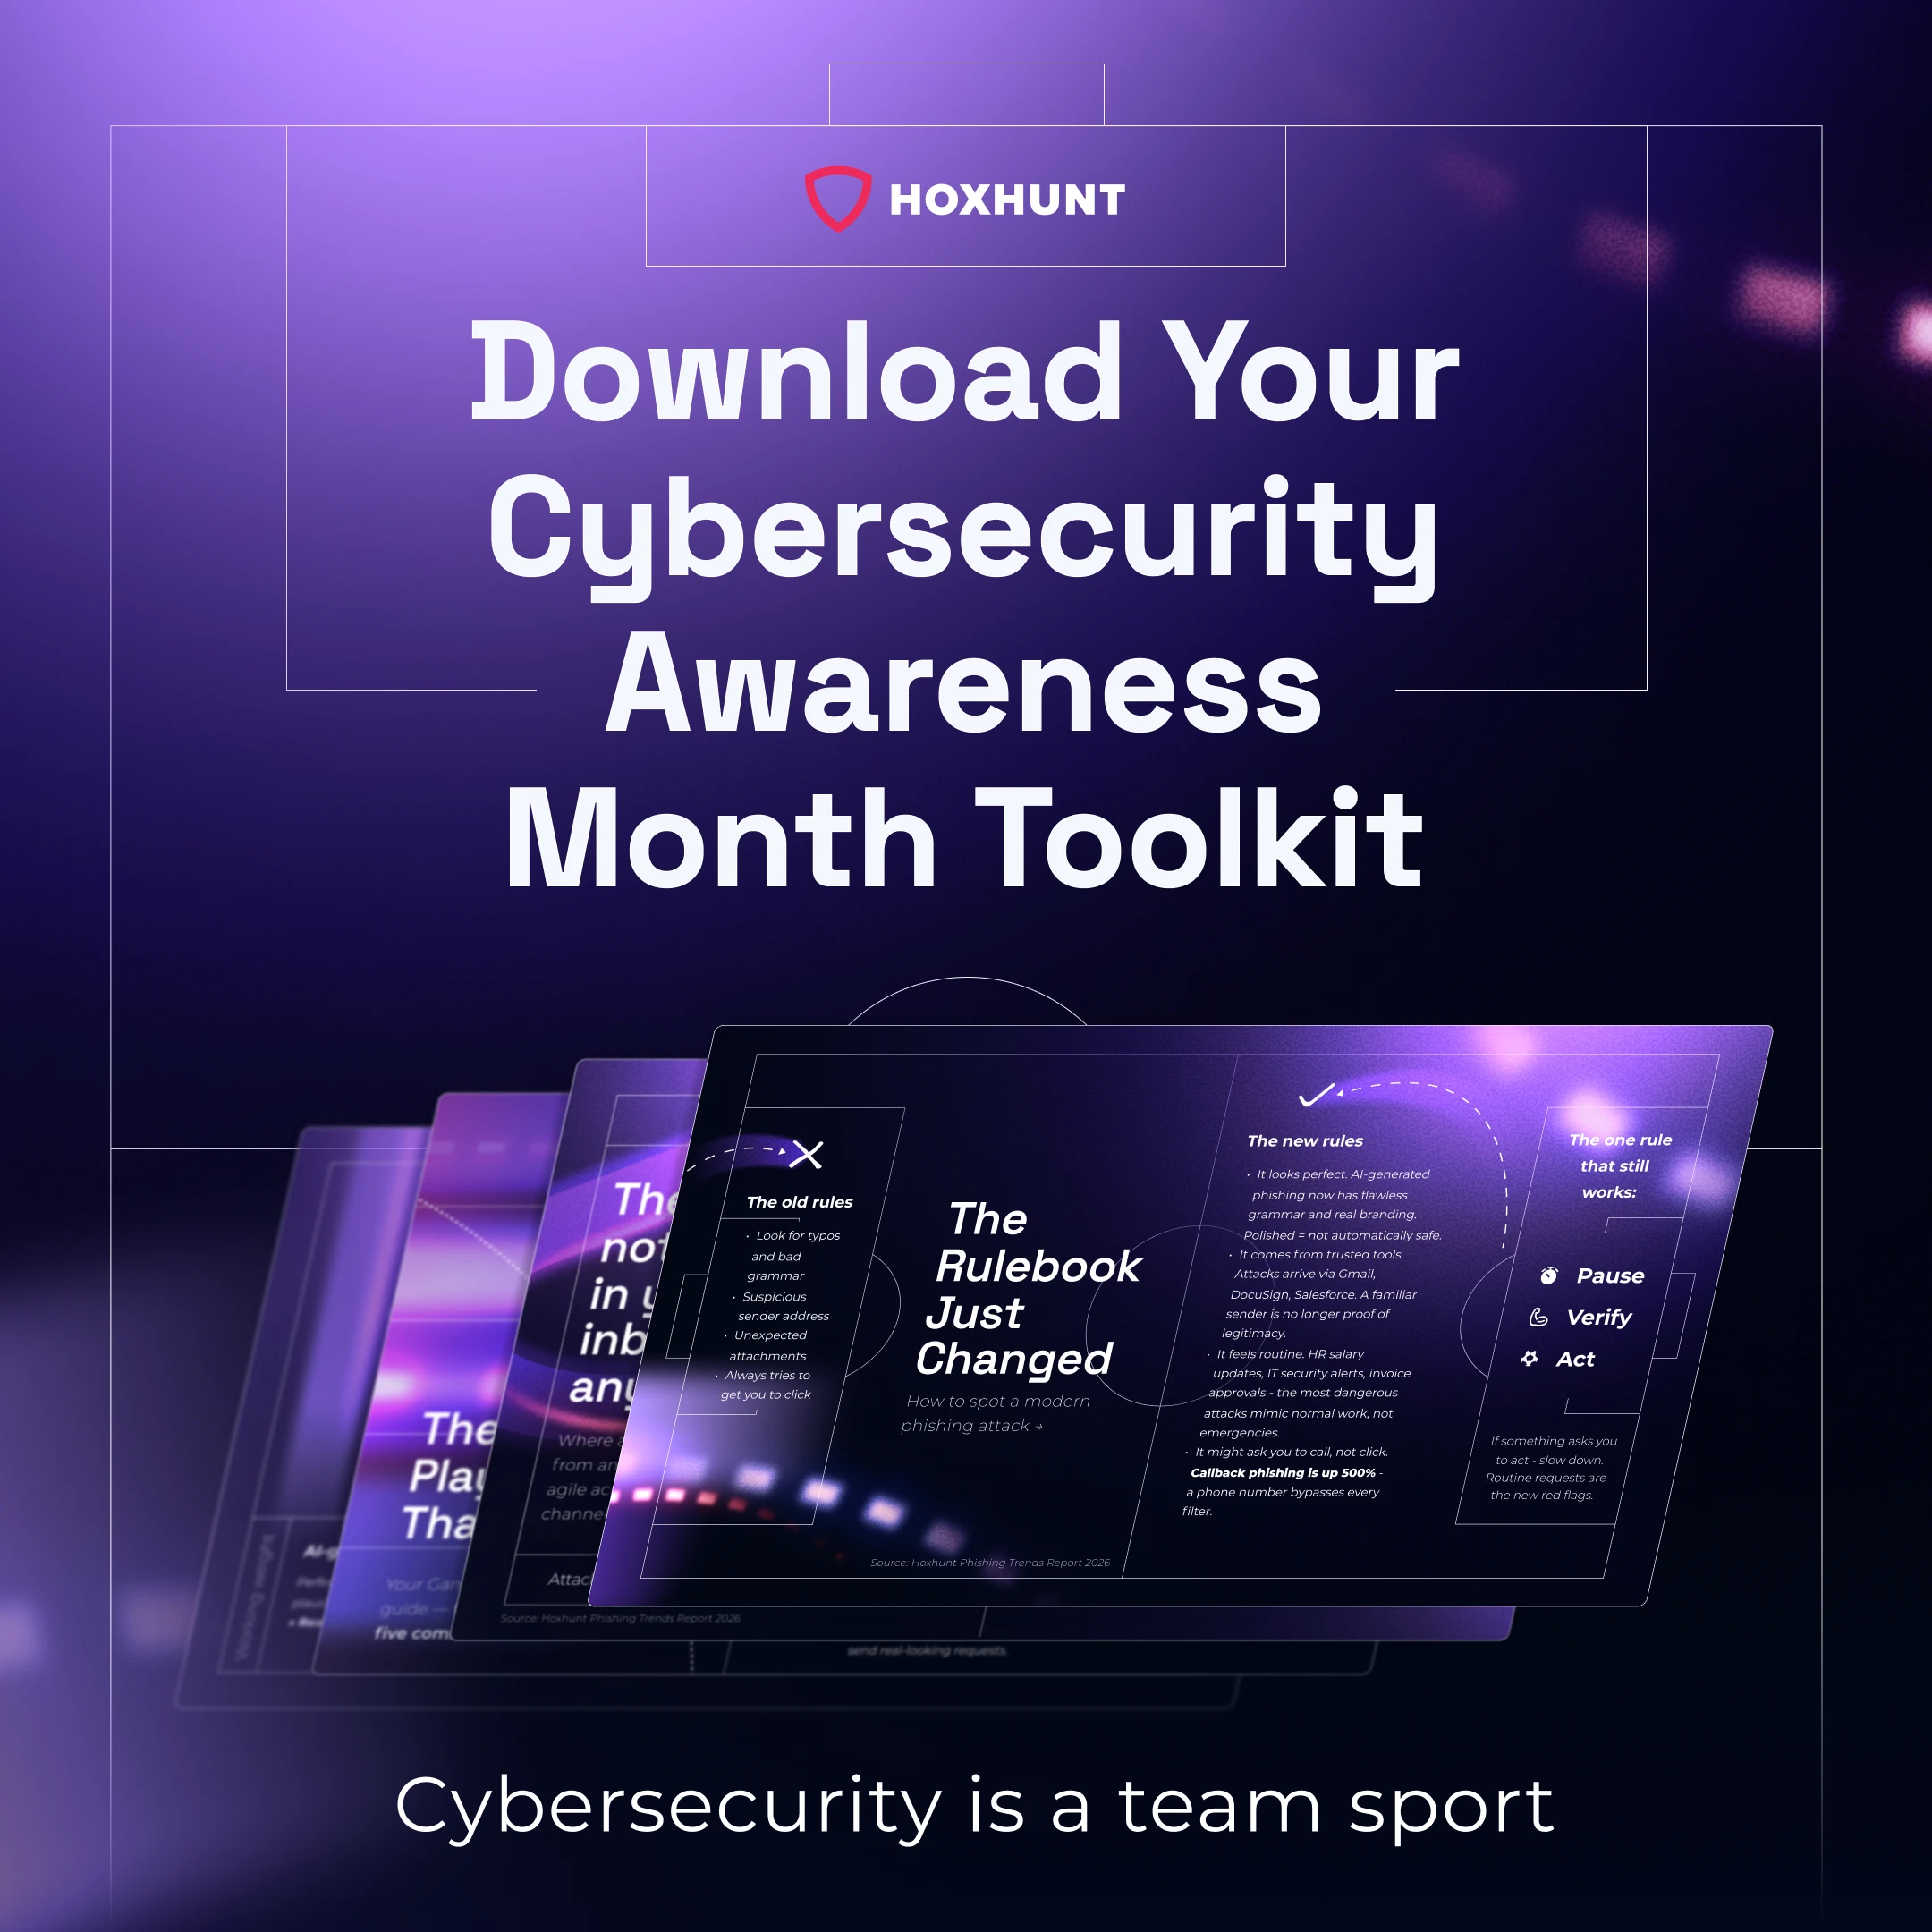
Our 2026 Cybersecurity Awareness Month Toolkit gives you four weeks of content built around “Cybersecurity is a team sport”:
- Four short, expert-led videos on deepfake phishing, generative AI attacks, and Slack-based social engineering
- Custom infographics that work as posters, screensavers, or digital shares
- Plug-and-play communications for email, Slack, and Teams
- Weekly interactive challenges employees can join without a Hoxhunt subscription
What is Cybersecurity Awareness Month 2026?
Cybersecurity Awareness Month is the October campaign, launched in 2004 and led today by CISA and the National Cybersecurity Alliance (NCA), that helps people and organizations protect themselves online. In 2026 it kicks off on October 1 and runs through the month, with two official themes: CISA’s “Securing the Next 250” and the NCA’s “Don’t Make It Easy for Them.”
For a security team the month is a window of attention you get once a year: Leadership expects something visible, employees expect something new, and both official organizers publish free materials you can build on. Three questions come first: what the month is, what this year’s themes ask of a workplace campaign, and what to run week by week. The rest of this guide answers them in that order, then shows how to prove the campaign changed behavior.
What is the Cybersecurity Awareness Month 2026 theme?
There are two official 2026 themes, one from each organizer. CISA’s theme is “Securing the Next 250,” tied to the United States’ 250th anniversary and aimed at the country’s digital defenses for the years ahead. The NCA’s theme is “Don’t Make It Easy for Them,” a call to make life difficult for cybercriminals.
For your workplace campaign the two themes point the same way: Make the basic protective behaviors easy and visible. Reporting a suspicious message, turning on multi-factor authentication, using a password manager, and pausing before a QR code or an urgent request are the behaviors both themes reward, so build your weekly themes around them.
Hoxhunt’s toolkit runs on its own line: “Cybersecurity is a team sport.” It is not an official theme; it is how we make the official themes fun to play. Awareness training usually feels like an exam you sit alone. Run October as a season instead: every report is an assist that protects the colleague who would have clicked, the phishing tournament and Phish-a-Friend give teams something to compete in, and the end-of-month quiz becomes the final rather than the test. Nobody fails alone, and the win belongs to everyone who reported.
10 Cybersecurity Awareness Month ideas 2026
Ten activities, each with the details that make it land. Mix two or three per week rather than running all ten; the plan after this list shows how.
1. Launch cybersecurity awareness posters that actually get noticed
Awareness posters are a low-lift, high-visibility way to make Cybersecurity Awareness Month tangible across your office or digital workplace. Simply plastering walls will not cut it: Rotation, branding, and relevance are what turn posters from background noise into behavior cues. (You can grab ready-to-use posters from our toolkit.)
Tie visuals to your campaign brand
- Align the design to the specific themes you’re covering, ideally the threats your organization is actually facing right now.
- Use consistent typography, colors, and taglines across posters, intranet tiles, and Teams backgrounds so employees instantly recognize the campaign.
Rotate weekly to avoid fatigue
- Engagement drops fast if the same poster sits for four weeks. Swap visuals every 7–10 days to keep attention fresh.
- Consider staging them. Example: Week 1 = phishing emails, Week 2 = multi-factor authentication, Week 3 = social engineering tactics, Week 4 = data privacy.
Make them actionable rather than decorative
- Add QR codes linking directly to short security awareness training modules, or use the codes themselves as phishing simulations to teach employees about the risk of scanning.
- Pair posters with microlearning tiles or a cybersecurity quiz so employees see and act in one flow.
Extend beyond physical spaces
For remote and hybrid teams, repurpose posters as:
- Screensavers and Teams and Slack backgrounds
- Digital infographics on the intranet or newsletters
- Animated tiles on shared screens in high-traffic areas
2. Host a lunch-and-learn (virtual + hybrid ready)
Lunch-and-learns are a time-tested way to build a cybersecurity culture without feeling like mandatory training. They work because they blend community, food, and learning (and they’re easy to adapt for hybrid teams).
Keep sessions short and focused
- Aim for 20–30 minutes, enough to grab attention without dragging.
- Focus on one pressing topic, such as phishing scams, malicious AI deepfakes, or multi-factor authentication adoption, so employees leave with one clear behavior to practice.
Make it interactive
- Encourage open Q&A. Many employees hesitate to ask “basic” security questions. So, normalize curiosity so your Security Team feels approachable.
- Use polls or a quick cybersecurity quiz to break up the format and reinforce recall.
Hybrid engagement tips
- For in-office sessions, provide free lunch to boost attendance.
- For remote teams, you could try sending digital coffee cards so everyone feels included.
- Record the session for those in different time zones, but keep it live where possible. The interactivity is what drives retention.
Use real stories as well as slides
- Invite a cybersecurity expert or internal champion to share a recent phishing incident, data breach, or social engineering attempt.
- Storytelling (“cyber horror stories”) sticks far longer than compliance decks because employees remember narratives.
3. Make noise on internal channels (intranet, Teams, Slack)
Cybersecurity Awareness Month only works if people see it consistently. That means leveraging internal communication channels beyond email to keep security top of mind without overwhelming employees.
Use a branded campaign identity
- Create a visual theme tied to Cybersecurity Awareness Month and this year’s official themes.
- Carry this branding across intranet banners, Microsoft Teams backgrounds, and digital signage.
Diversify formats for different attention spans
- Microlearning tiles (30–60s clips) covering things like phishing scams, multi-factor authentication, or data privacy basics.
- Infographics for quick security posture reminders.
- Cybersecurity quiz prompts as polls on Slack or Teams to spark interaction.
Leverage leadership voices
- A short executive kickoff video adds credibility.
- Provide manager comms packs with copy-paste blurbs so line managers can cascade messages to their teams.
Nudge the right behaviors
- Every channel post should include a clear call-to-action.
- Rotate weekly to keep content fresh and engaging.
4. Host a cybersecurity movie night (with a learning twist)
A movie night may not sound like a typical cybersecurity awareness training tactic, but it’s a proven way to make Cybersecurity Awareness Month fun, memorable, and team-building.
Pick engaging, security-themed films
- Classics like Hackers (1995), The Net (1995), or The Matrix (1999) highlight the cultural side of cybersecurity threats.
- For a different vibe, Tron (1982) demonstrates the chaos that malicious programs can cause.
Add a quick debrief to tie it back
- After the screening, spend 5–10 minutes linking themes to real-world security incidents.
- Example prompts:
- The Net: password hygiene and identity theft
- Hackers: phishing scams and insider threat actors
- The Matrix: data privacy and the evolving threat landscape
Keep it inclusive and hybrid-friendly
- Offer a streaming option so remote employees can join.
- Make participation optional to avoid fatigue.
- Encourage informal discussion in a Slack or Teams channel so the conversation extends beyond the film.
5. Phish your employees (go beyond email)
Phishing simulations remain the backbone of cybersecurity awareness programs but Cybersecurity Awareness Month is your chance to expand beyond email and test real-world social engineering tactics.
Start with multi-channel phishing simulations
- Email phishing is still the baseline, but employees increasingly encounter threats like smishing or QR code phishing.
- Physical prompts work too: in E.ON’s “Don’t Scan” QR campaign, 70% of survey respondents saw the QR codes and did not scan them.
Emphasize reporting over “not failing”
- Standardize a single “Report a Phish” button across channels to reduce confusion.
- Coach immediately after a click and celebrate every report: Time to report is the number that matters.
Gamify with tournaments and peer-generated lures
- Run an opt-in phishing tournament during October with points for timely reporting.
- Try a “Phish-a-Friend” challenge where employees submit realistic lures that the Security Team adapts into safe simulations. At Hoxhunt, we built our Phish-a-Friend feature so employees can send simulations to each other, which creates friendly competition and makes things fun.
- Keep the campaign short (10–14 days) to prevent fatigue, even when people enjoy the competition.
Tie results back to business metrics
- Track changes in reporting rates, reporting speed, and risk levels by department.
- Share results with executives to show how Cybersecurity Awareness Month improves the organization’s security posture beyond training completions.
Below you can see what simulations actually look like for users in the Hoxhunt platform.
6. Invite a speaker to tell cyber horror stories
Storytelling is one of the most powerful tools in security awareness training. Employees might forget numbers, but they remember a well-told story about how a phishing email or social engineering scam led to a breach.
Why stories work
- Narratives activate emotion and stick longer in memory than facts or compliance slides.
- A relatable cyber horror story makes online threats tangible, showing how easily mistakes escalate into security incidents.
Who to bring in
- External cybersecurity experts who can share high-profile case studies (phishing scams, ransomware, data breaches).
- Internal champions from your Security Team or IT department with firsthand stories about blocked phishing emails, insider risks, or near-miss social engineering tactics.
- Consider voices outside of security: Finance or HR leaders who’ve seen fraud attempts can provide a fresh perspective.
How to structure the session
- Keep talks to 20–30 minutes followed by Q&A.
- Use a real-world breach as a case study, then unpack what could have been prevented with MFA, a password manager, or faster reporting.
- Tie the story back to employees’ daily actions: reporting suspicious emails, not scanning rogue QR codes, and being skeptical of urgent requests.
Hybrid engagement ideas
- Record sessions for later replay in global offices.
- Clip highlights into short microlearning tiles to reinforce lessons throughout October.
7. Drive adoption of key security measures (MFA + password manager)
Changing passwords every 90 days is out of step with today’s cybersecurity best practices. A stronger play is using October to accelerate adoption of multi-factor authentication (MFA) and password managers, which directly reduce the risk from phishing scams and credential theft.
Run an MFA adoption challenge
- Encourage employees to enable MFA (two-factor authentication) on both corporate and personal accounts.
- Track adoption as a visible campaign metric beyond completions.
- Use nudges like “Secure your account in 60 seconds” and show employees how MFA blocks real-world phishing attempts.
Make password managers simple and personal
- Offer a company-wide license with a personal or family plan extension.
- Provide a step-by-step setup guide and a 15-minute drop-in session during Cybersecurity Awareness Month office hours.
- Position it as a convenience tool (fewer forgotten logins) as much as a security measure.
8. Create a cybersecurity-themed escape room (physical or digital)
Escape rooms are a gamified way to bring cybersecurity concepts to life during Cybersecurity Awareness Month. They transform abstract risks into puzzles employees can solve collaboratively.
Design puzzles around real-world threats
- Spotting phishing emails, QR codes, or smishing texts.
- Cracking strong password rules or demonstrating password manager use.
- Telling secure from insecure Wi-Fi connections or cloud storage practices.
- Escaping only after “reporting” a suspicious message correctly.
Keep it short and accessible
- Sessions should run 20–25 minutes to respect employees’ time.
- Limit group sizes to 4–6 people to keep everyone engaged.
- Make participation opt-in: Forced fun creates fatigue.
Go hybrid with virtual rooms
- Use online puzzle platforms for distributed teams.
- Incorporate “choose your own adventure” storylines featuring cyber horror stories like data breaches or insider threats.
- Pair digital escape rooms with cybersecurity quiz elements for extra reinforcement.
Reinforce behavior with coaching
- Debrief each group on what the puzzles represented in the real threat landscape.
- Connect back to your Security Team’s reporting workflow.
9. Introduce cybersecurity office hours
Many employees hesitate to engage with the Security Team until it’s too late. Office hours create a recurring, judgment-free space where staff can ask questions and get guidance during Cybersecurity Awareness Month.
Why office hours work
- Normalize “asking early” about phishing scams, suspicious links, or MFA issues.
- Reduce risky workarounds like shadow IT by offering trusted alternatives.
- Show the IT department as a partner rather than a gatekeeper.
How to set them up
- Dedicate 30 minutes each week during October.
- Offer both in-person and virtual slots to include hybrid teams.
- Promote them on intranet, Teams, and email to maximize visibility.
What to cover
- Walkthroughs of the “Report a Phish” button or phishing simulation results.
- Quick help with password manager installs or multi-factor authentication enrollment.
- Live demos of recent cybersecurity threats, like voice phishing or malicious AI deepfakes, and how employees can spot them.
Keep the culture going year-round
- Extend monthly office hours beyond October as part of your ongoing cybersecurity awareness program.
- Rotate themes, for example data privacy, secure cloud storage, or new attack channels.
10. Run a cybersecurity quiz at the end of the month
A quiz is a simple yet powerful way to reinforce security awareness training and celebrate Cybersecurity Awareness Month. Done right, it turns learning into a game employees actually want to play.
Keep it competitive (but fun)
- Use a leaderboard with small prizes or digital badges.
- Offer team challenges where departments compete on phishing detection or password hygiene.
- Keep rounds short: 10–15 questions max.
Cover the right topics
- Spotting phishing emails and smishing messages.
- Why multi-factor authentication and password managers matter.
- Recognizing social engineering tactics and malicious AI deepfakes.
- Core data privacy habits employees can apply at work and home.
Gamify for higher engagement
- Gamified cyber security training works. So, introduce gamified elements into your awareness-raising efforts to engage employees and make the learning experience something people can actually enjoy.
- Add capture-the-flag elements (solving a staged security incident).
- Give bonus points for fastest reporting rate of simulated phishing emails.
- Pair the quiz with a microlearning tile or infographic to reinforce key takeaways.
Use results to guide next steps
- Identify departments with weaker detection capabilities.
- Share quiz highlights in internal comms to close the campaign on a high note.
- Feed insights into your year-round cybersecurity awareness program.
You can see what Hoxhunt’s gamification looks like in the interactive demo below.
A 4-week Cybersecurity Awareness Month plan
One theme a week keeps the campaign readable for employees and gives you one metric to report per week. Concentrate the heavy activities, the simulations, the executive video and the live sessions, in a ten-business-day core across weeks two and three, and keep weeks one and four lighter. Uber’s Cybersecurity Awareness Month engagement rose 50% year over year, with a 50% rise in attendance at its live sessions.
| Week | Theme | Activity | Metric |
|---|---|---|---|
| Week 1 (Oct 1 to 3) |
|
|
|
| Week 2 (Oct 6 to 10) |
|
|
|
| Week 3 (Oct 13 to 17) |
|
|
|
| Week 4 (Oct 20 to 31) |
|
|
|
The CISA toolkit and the NCA kit cover weeks one and three (reporting phishing, passwords and multi-factor authentication); neither covers week two’s channels or week four’s measurement. The Hoxhunt toolkit brings a ready-made drop for each of the four weeks (a short video, a message, an infographic and a challenge), with themes that run from multi-channel threats to AI-generated attacks. Use it as the content and keep this plan as the calendar.
What is new in 2026: AI voice, deepfakes, QR and Teams phishing
The lures employees see in 2026 have moved off email. Voice calls generated with AI, deepfake video of executives, QR codes on posters and parcels, and fake Microsoft Teams notifications are where this year’s lures have moved. The NCA’s theme says it plainly: The easiest way to “make it easy for them” is to assume a threat only ever arrives by email.
Use the live lures from Hoxhunt’s threat posts as the content for week two, and link them in your internal comms so employees see what the real thing looks like:
- Vishing attacks: AI voice phishing and how to train people to hang up and verify.
- Deepfake attacks: video and audio impersonation of leaders.
- Quishing: QR code phishing, the channel E.ON built its “Don’t Scan” campaign around.
- Microsoft Teams impersonation: the fake “teammates trying to reach you” notification.
For the rest of the year’s topics, the security awareness topics for employees list is the companion to this page.
Campaign planning & execution tips
Running Cybersecurity Awareness Month well means designing for impact and sustainability rather than stacking as many activities as possible. Here’s how security leaders are planning smarter campaigns in 2026.
Focus on a 10-day burst rather than 4 weeks straight
- Engagement decays sharply after week two.
- Concentrate phishing simulations, exec videos, and lunch-and-learns into a 10-business-day core, with lighter activities before and after (weeks two and three in the plan above).
- This avoids awareness fatigue while still honoring the full October calendar.
Manage fatigue with quality over quantity
- Avoid spamming every channel every day: Fatigue reduces learning.
- Rotate themes weekly.
- Design content that’s inclusive: multilingual, accessible formats, time-zone aware.
Enable managers and internal champions
- Equip managers with ready-to-send comms packs so they can cascade key messages.
- Create a Champion program where volunteers model reporting and share stories.
- Partner early with Internal Comms so your campaign feels polished rather than improvised.
Plan the handoff to Data Privacy Week
- Don’t let momentum die on November 1.
- Tease follow-up activities that connect October’s lessons to data privacy and personal online safety.
- Extend office hours or quizzes into privacy clinics to show security culture is year-round.
Mistakes to avoid
- Treating October as the program: A month of activity with nothing before or after it reads as a compliance exercise, and employees treat it as one.
- One poster for four weeks: Visuals that never change become wallpaper by week two; rotate them every seven to ten days.
- Every channel, every day: Attention is the budget. Spend it on the ten-day core and keep the rest of the month light.
- Measuring completions: Completion rates show who clicked through a module; reporting rate and time to report show who changed behavior.
- Going quiet on November 1: Announce the hand-off to Data Privacy Week and the year-round office hours while the campaign is still live.
Whether you’re running the campaign as a full team or flying solo, the webinar Cybersecurity is a team sport: October is the big game walks through real-world-tested ideas that boost engagement and change behavior.
Metrics that matter (board-ready outcomes)
Running engaging activities in October is only half the job: Leaders expect evidence of impact. Security awareness managers who report on the right outcomes win credibility with executives and boards.
Reporting rate & time-to-escalation
- Reporting rate shows how many employees spotted and flagged a phishing email or smish.
- Time-to-escalation reveals how quickly incidents get to the Security Team once detected.
- Together, these metrics demonstrate resilience rather than awareness alone.
What counts as a good reporting rate? Employees in quarterly security awareness training report roughly 10% of simulations, according to the Hoxhunt Phishing Trends Report 2026. Verizon’s DBIR 2024 and 2025 put the global benchmark at around 20%. Above 20% is the mark of a behavior change program and a mature security culture. Use October to get past that line.
10%
of phishing simulations get reported when employees only get a quarterly awareness training course
Source: Hoxhunt Phishing Trends Report 2026, p. 33
55.3%
of phishing simulations get reported three months into a Hoxhunt program
Source: Hoxhunt Phishing Trends Report 2026, p. 38
MFA & password manager adoption
- Track the number of accounts protected by multi-factor authentication during and after the campaign.
- Measure uptake of the password manager rollout, including family plans if offered.
- These adoption metrics are clear proof of lasting behavior change.
Executive dashboard
Summarize results in one board slide:
- Activities delivered
- Key metrics (reporting rate, adoption, incidents)
- Risk reduction narrative
- Keep it outcome-driven: what changed, how fast people report, what adoption moved.
You can explore Hoxhunt’s reporting dashboard below.
Free Cybersecurity Awareness Month resources and toolkits
Both organizers and two public bodies publish free material every year. Start here before you design anything; the Hoxhunt toolkit adds the videos, visuals, messages and challenges made for a workplace campaign.
| Resource | What you get | Best used for |
|---|---|---|
| CISA Cybersecurity Awareness Month 2026 Toolkit |
|
|
| National Cybersecurity Alliance |
|
|
| NIST Cybersecurity Awareness Month |
|
|
| SANS workforce security resources |
|
|
| Hoxhunt Cybersecurity Awareness Month Toolkit 2026 |
|
|
Hoxhunt Cybersecurity Awareness Month Toolkit 2026
We’ve built the toolkit for security leaders who want to run a high-impact campaign without starting from scratch. Deploying each week takes about 15 minutes.
Want the best awareness month you’ve ever run? You don’t need a big budget, a big comms team or a Hoxhunt subscription. Download the complete 2026 Cybersecurity Awareness Month Toolkit, a campaign-in-a-box built on years of award-winning campaigns from companies like Docusign and Qualcomm, and run a professional, engaging October that generates measurable results without the extra workload.
Is it time to switch up your security awareness training?
October ends; the behaviors you built should not. A month-long campaign is the easiest moment of the year to notice whether your security awareness training is measurably reducing human risk or only checking a compliance box. If reporting rose during the campaign and falls back in November, the program is the problem, and October has handed you the evidence.
The Hoxhunt Phishing Trends Report 2026 shows what a behavior change program looks like after the burst: Three months into a Hoxhunt program, employees sit at a 6.0% failure rate. That is the number to put next to your October results when you decide what the next eleven months look like.
- Keep the cadence: Move from one October burst to short, regular simulations across channels, so reporting becomes a habit rather than an event.
- Keep the measures: Reporting rate, time to report and MFA adoption are the same three numbers in November as in October; a dashboard that only exists for the campaign disappears with it.
- Keep the people: The champions, the office hours and the manager comms packs are the year-round program’s infrastructure. How to build it is in the security awareness training program guide; where it fits in the wider picture is in the human risk management playbook.
Below, a look inside the Hoxhunt platform.
Cybersecurity Awareness Month Ideas FAQ
Short answers to the questions security teams ask most while planning October.
What is Cybersecurity Awareness Month?
Cybersecurity Awareness Month is the global campaign that runs every October, launched in 2004 and led today in the United States by the National Cybersecurity Alliance and CISA. For a business it is the one month a year when leadership, IT and employees are all paying attention to the same topic, which makes it the best moment to change a behavior and measure the change.
When is Cybersecurity Awareness Month 2026?
October 2026. The NCA kicks the month off on October 1, 2026, and campaigns run through October 31.
What is the Cybersecurity Awareness Month 2026 theme?
There are two official 2026 themes: CISA’s “Securing the Next 250” and the National Cybersecurity Alliance’s “Don’t Make It Easy for Them.” Hoxhunt’s toolkit uses its own campaign line, “Cybersecurity is a team sport,” which is a framing for the workplace campaign rather than an official theme.
Is Cybersecurity Awareness Month only a US campaign?
No. The NCA describes it as a global initiative, and several countries run their own October campaigns: Canada’s Cyber Security Awareness Month is led by the Communications Security Establishment with the 2026 theme “Your best defence is you,” and Australia runs Cyber Security Action Month through the Australian Cyber Security Centre. If you have offices in those countries, align week one with the local campaign’s messaging.
Should our campaign run the full month, or just 10 days?
Keep the official month as your frame and concentrate the heavy activities in a ten-business-day core. Simulations, the executive video and the live sessions land best while attention is high; lighter touchpoints such as posters, office hours and the quiz carry the rest of October.
How do we avoid awareness fatigue?
Rotate one theme a week, keep each activity short, and leave channels quiet between pushes. Make the social activities opt-in, and design the content for every office: multiple languages, accessible formats and time-zone aware scheduling. Fewer, better touchpoints build behaviors that last.
What are the easiest activities to launch quickly?
Posters, a short quiz and a lunch-and-learn can all be live within days using the CISA and NCA materials or the Hoxhunt toolkit. Phishing simulations across email, text and Teams add the most impact if you already have the tooling in place.
Should we include Microsoft Teams or Slack phishing?
Yes. Employees meet phishing on collaboration platforms too, and a single well-placed Teams simulation shows blind spots that email simulations miss. Coordinate with Internal Comms first so a real alert is never mistaken for training.
How do we talk about malicious AI and deepfakes without causing fear?
Present them as new delivery channels for familiar tricks, demonstrate one in a short clip or a lunch-and-learn, and end on the actions that neutralize them: report the message, keep multi-factor authentication on, and confirm unusual requests through a second channel.
What free Cybersecurity Awareness Month resources are available?
The CISA Cybersecurity Awareness Month 2026 Toolkit, the National Cybersecurity Alliance’s Champion program and toolkit, NIST’s awareness month pages and SANS’s awareness kits are all free. Hoxhunt’s Cybersecurity Awareness Month Toolkit 2026 adds four weeks of workplace-ready videos, visuals, comms templates and challenges, also free.
What should we measure to prove impact?
Reporting rate and time to report from your simulations, adoption of multi-factor authentication and the password manager, and the trend in reported incidents against previous months. Put them on one executive slide; completion rates alone do not show that behavior changed.

Get more cybersecurity insights like this
- Subscribe to All Things Human Risk to get a monthly round up of our latest content
- Request a demo for a customized walkthrough of Hoxhunt