



What is Human Risk Management in cybersecurity?
The short answer
Human Risk Management (HRM) is the practice of identifying, measuring, and reducing security risks caused by human behavior, such as falling for phishing emails, mishandling sensitive data, or bypassing security controls. It’s built for CISOs, security awareness managers, and SOC teams who need measurable behavior change, not just compliance. HRM matters now because remote work, AI-powered social engineering, and new regulatory pressures have made people the largest and fastest-changing attack surface in cybersecurity.
Before you choose a platform, it helps to be clear on what actually reduces human risk in the first place.
If the question is how to stand the program up rather than which platform to buy, our guide to building a security awareness training program covers the baseline, the metrics and the first 90 days.
Key takeaways
- Human risk management is the successor to security awareness training: it measures and changes risky behavior instead of counting course completions.
- Every major analyst now defines the category around one word, behavior. Outcome-driven metrics are how you prove it is changing.
- Start where the risk is, phishing and social engineering. Threat reporting is the first behavior to build, measure and reward.
- Four outcome-driven metrics matter most: reporting rate, failure rate, real-threat detection and dwell time. Resilience ties them together.
- The results compound. Engagement rises roughly sixfold within six months and real-threat reporting climbs ninefold, per the Hoxhunt Phishing Trends Report 2026.
- Human threat intelligence belongs in the SOC. Connect training output to incident response and the whole stack gets faster.
- Reward, do not punish. Psychological safety and gamification drive the engagement everything else depends on.
What do Gartner, Forrester, and Frost & Sullivan say about human risk management?
Three analyst houses now cover this category, and all three frame it around measurable behavior change rather than training delivered. Where they part company is whether phishing and social engineering outcomes count toward the score at all, and they do not even agree on what to call it.
Forrester published its first Wave for Human Risk Management Solutions in Q3 2024, evaluating nine providers against 35 criteria.
Gartner covers the same ground under its own category name, Security Behavior and Culture Programs, which it frames around measurable behavior rather than training delivered.
Frost & Sullivan recognised Hoxhunt for Competitive Strategy Leadership in the human risk management industry, and tracks the category in its Customer Transformation Journeys report.
The same platform, doing the same work, can top one framework and lag the other. So before you let a ranking build your shortlist, read the rubric behind it, and ask which behaviors it scored and which it left out. Hoxhunt reports against all three definitions, covering behavior tracking, targeted interventions, and cultural metrics.
Core functions of Human Risk Management:
- Behavioral measurement: Track risky actions and security habits in real time.
- Outcome-driven metrics: Prove reduced risk through data, not just training completions.
- Adaptive training: Personalize interventions for high-risk individuals.
- Threat intelligence integration: Feed employee-reported incidents into SOC workflows.
We went deep on measuring real behavior change instead of just awareness in a recent episode of the All Things Human Risk Management Podcast, unpacking how organizations can move from tick-box training to genuine risk reduction.
Why should security leaders adopt Human Risk Management now?
2024 was the year Human Risk Management came into its own. Finally enshrined as its own category, independent of security awareness training, HRM promises to deliver greater return on investment than any other strategic security initiative.
Why? Because for cyber criminals, the human layer is where the money’s at: social engineering, phishing, and insider threats comprise the greatest risk for multi-million-dollar data breaches, according to IBM. And those threats are getting worse by the day in the age of AI, according to the Verizon DBIR. How much worse? The Hoxhunt Phishing Trends Report 2026 recorded the AI share of reported attacks soaring from 4% to 56% across the Hoxhunt global threat detection network over a single holiday season.
Consequently, the HRM platform you choose must be designed to reduce risk starting at its greatest source, social engineering and phishing. An effective HRM platform will produce measurable behavior change that reduces risk by connecting threat detection, meaning recognizing and reporting phishing attacks, between the real and the simulated environments. Integrating human threat intelligence into the security stack makes it possible to stop threats before they can spread.
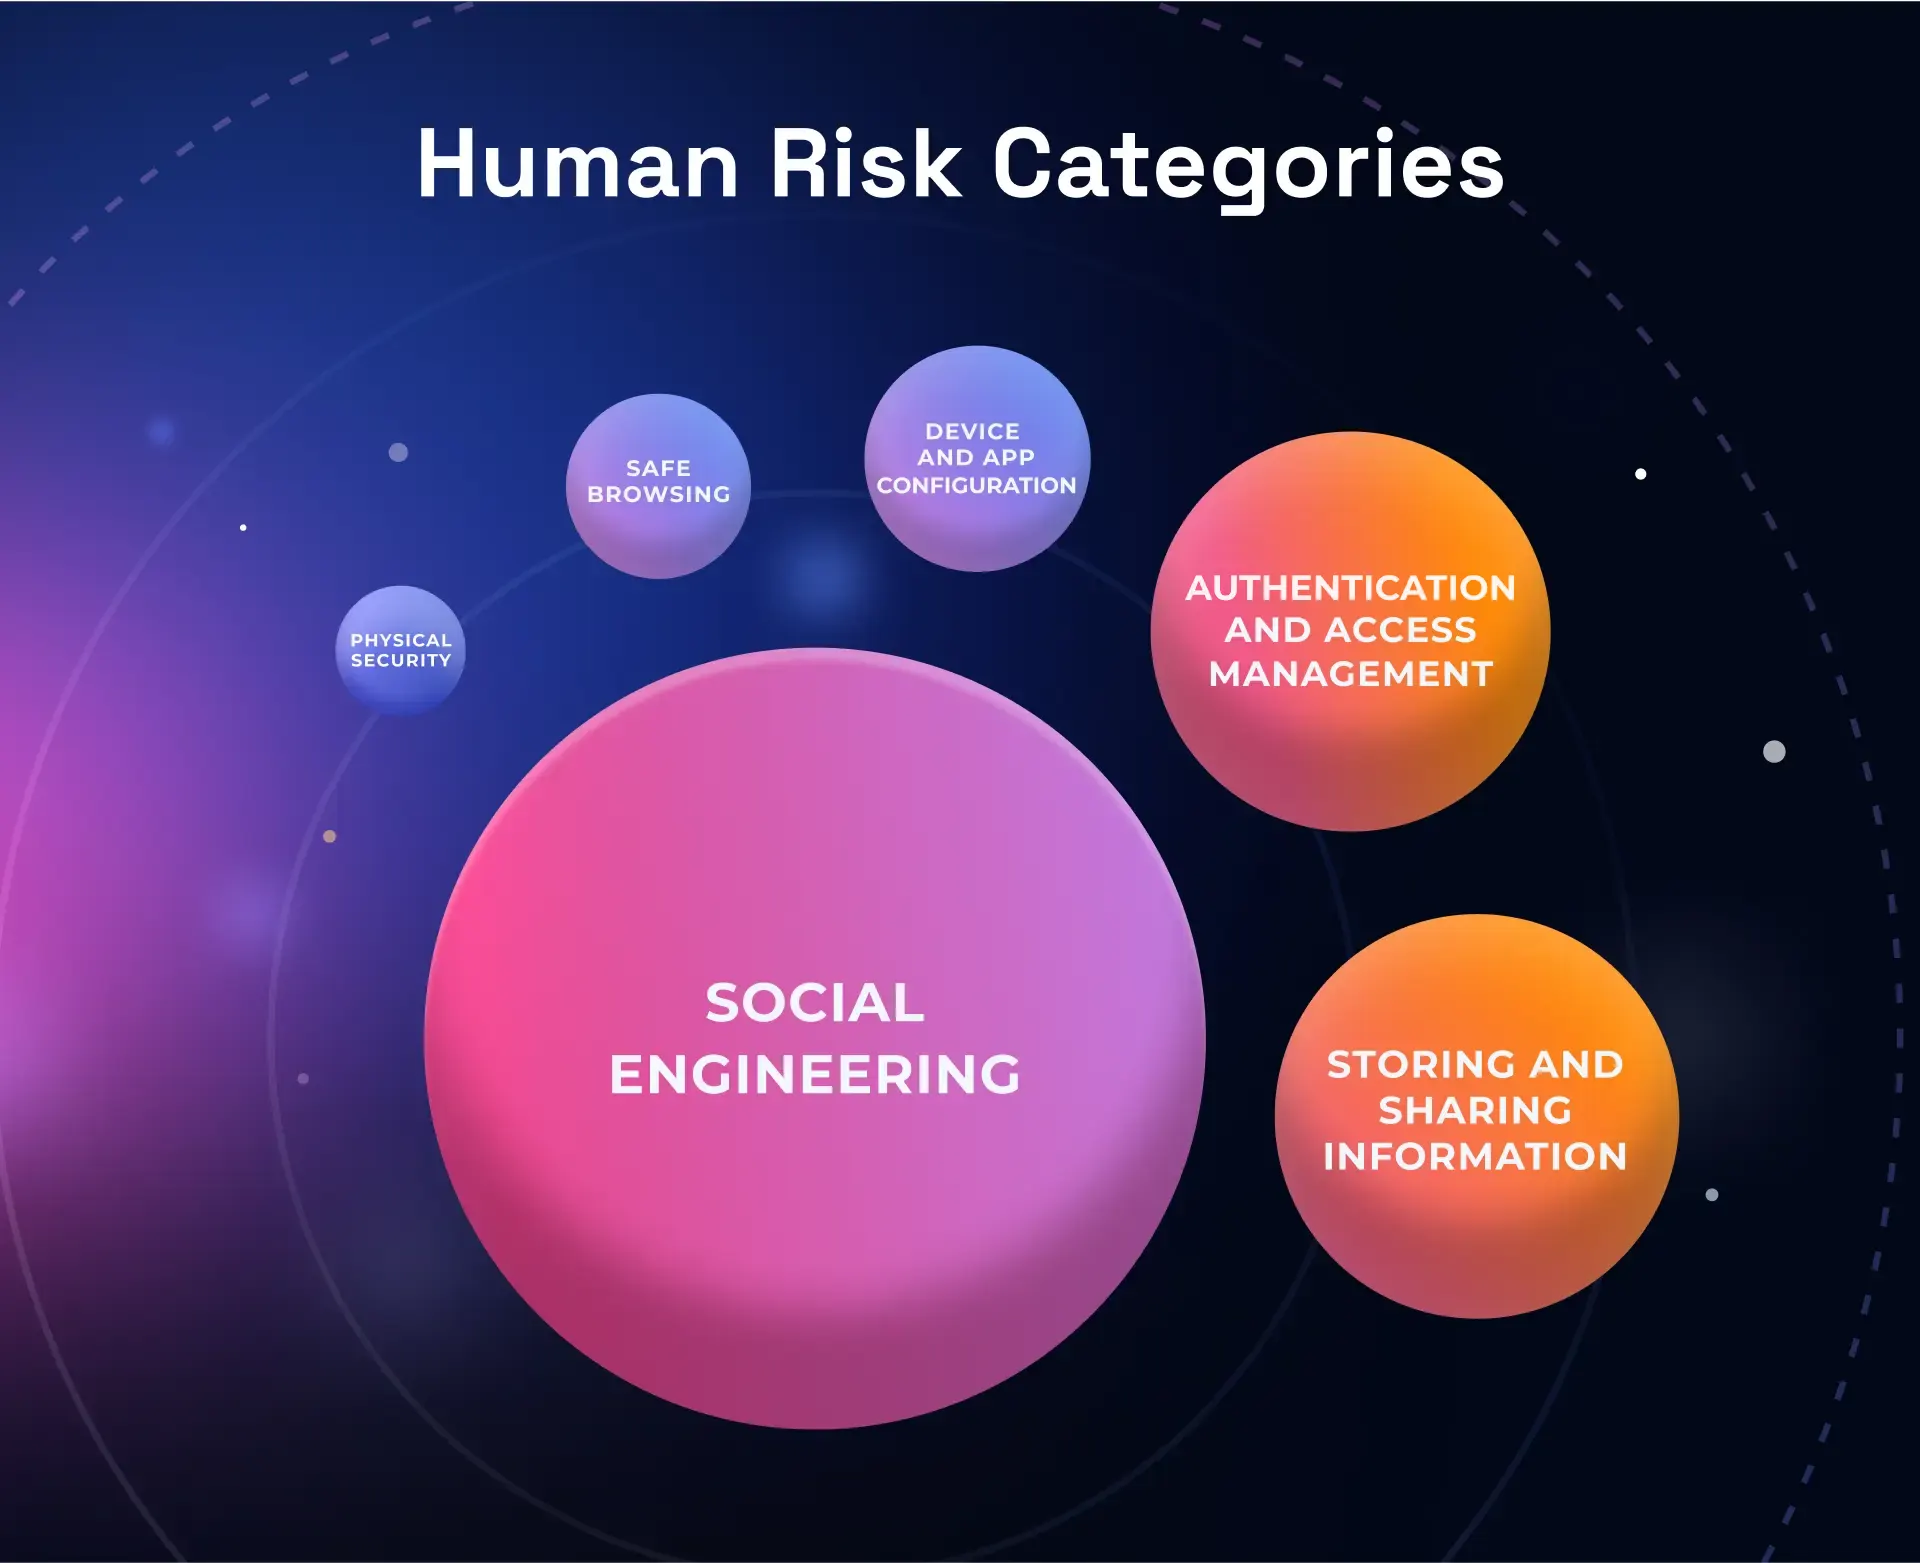
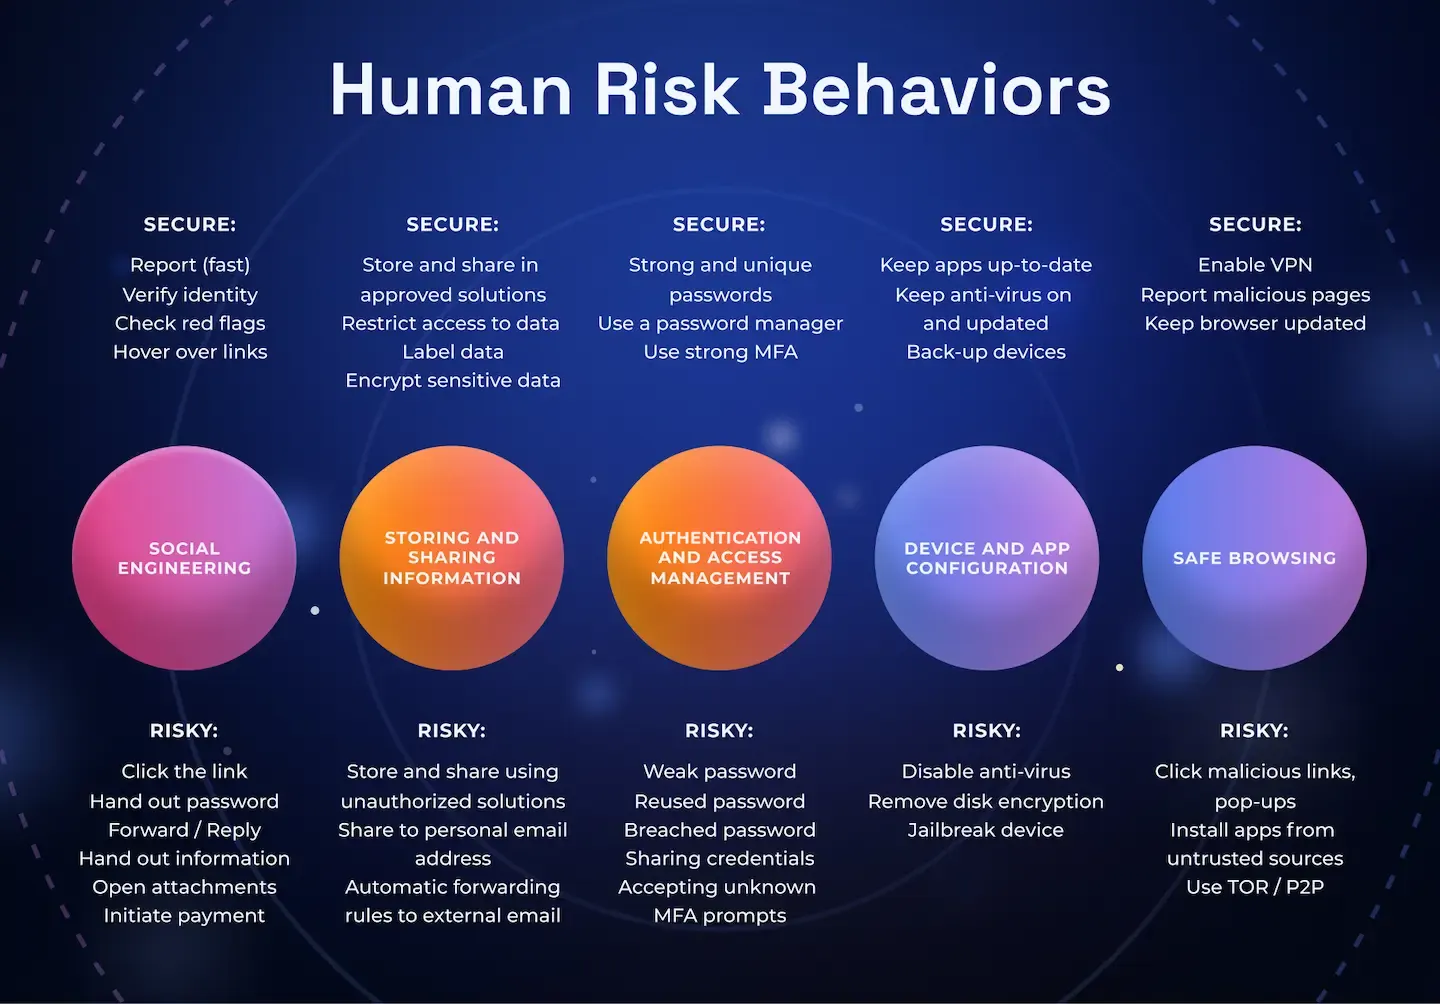
But HRM needn’t stop at social engineering. This risk-based approach can be applied to a broad range of behaviors including: Storing and sharing information; authentication and access management (e.g. MFA); timely security updates; and safe browsing.
The basic principles of a human risk-based approach can be applied to all of these behaviors through behavioral signal-based nudge alerts that trigger an admin response, automatic mitigation, or a targeted micro-training.
Every major analyst has published, or is about to publish, its own report on HRM, each with its own evaluation criteria. The differences can be fundamental. Forrester, for instance, focuses on the breadth of security awareness content and omits social engineering and phishing outcomes from their wave report’s human risk management criteria.
Meanwhile, Gartner focuses on social engineering and phishing outcomes as core to reducing human risk in their post-awareness-training category, Security Behavior and Culture Program (SBCP).
The unifying thread? In a word: “behavior.” Human Risk Management Platforms correct risky behaviors at scale to measurably build culture and reduce human risk.
Let’s pause on the word “measurable.” Whereas yearly or quarterly security awareness training was geared for education and compliance, HRM is defined by outcome driven metrics (ODM) that demonstrate:
- Behavior change
- Cyber skills and habits acquisition
- Increased resilience
- Decreased risk across the human layer
- Real world impact
The key to HRM is ODM. Any platform claiming to be Human Risk Management must demonstrate outcome driven metrics relevant to reducing human cyber risk.
How have AI and remote work made Human Risk Management a priority for security leaders?
Human Risk Management is essential today because AI phishing attacks, remote-work vulnerabilities, and advanced social engineering have outpaced traditional security awareness training. HRM platforms like Hoxhunt combine real-time behavioral data, adaptive training, and integrated threat intelligence to reduce human cyber risk, protect against multi-channel attacks, and strengthen security posture across distributed workforces.
Human Risk Management has risen from the ashes of security awareness training in 2024. It started back in 2020, when cyber crime and insider threats experienced a phase change with the pandemic-driven shift to the cloud and remote work. The ensuing multi-billion-dollar wave of ransomware, BEC, and spear phishing pushed the cyber insurance industry to the brink of collapse in 2021, and it has been volatile ever since.
Add in the 2022 rise of AI, and the threat landscape is more than security awareness training can handle. More and better-crafted threats are bypassing email filters every day. Social engineering alone is an omni-channel problem, as deep fakes and other highly sophisticated attacks become available on the dark web’s cybercrime-as-a-service market.
At that point, it’s up to people: admins and end users, alike. Everyone needs to be able to join forces on a Human Risk Management platform that provides just-in-time micro-training to behave securely, and the tools and seamless integrations that weave human threat intelligence into the security stack.
Threat landscape by the numbers
$4.8Maverage cost of a breach that starts with phishing, the most common initial attack vectorSource: IBM Cost of a Data Breach Report 2025
4,151%increase in malicious phishing messages sent since ChatGPT launched in November 2022Source: SlashNext Mid-Year State of Phishing Report, May 2024
Between 68% to 95% (WEF) of data breaches contain the human element, primarily via social engineering and phishing. Other costly risks include user and admin errors while handling sensitive information, as well as malicious insider acts, which the 2024 IBM Cost of a Data Breach report pegged at $4.99M.

Many believe the emergence of Human Risk Management is long overdue. The HRM movement has been developing since at least 2016, when Hoxhunt was founded to disrupt the compliance-based security awareness training model. Several thought leaders have been publishing articles since well before then calling for a more dynamic solution than security awareness training to stay secure in a swiftly tilting threat landscape.
Suddenly, many up-jumped security awareness training vendors are rushing into the HRM space and calling themselves Human Risk Management Platforms. But each analyst and vendor has their own criteria for HRM.
In all of our excitement, the discourse around HRM can get a little noisy. But you can separate the signal from the noise by prioritizing outcome driven metrics.
CISOs need to know: is the HRM platform measurably changing behavior and reducing risk? Am I mitigating the biggest risk cluster of all: people-targeted attacks like social engineering and phishing?
Human Risk Management vs. Security Awareness Training: what’s the difference?
Human Risk Management focuses on measuring and reducing human cyber risk through outcome-driven metrics, adaptive training, and integrated threat intelligence. Security Awareness Training is primarily compliance-driven, aiming to educate users on threats. HRM goes further by driving measurable behavior change and embedding security culture into daily operations.
In addition to measurably reducing risk, HRMs provide numerous benefits to business and security functions, including culture building, business continuity, C-suite reporting, GRC, and cyber insurance.
Human Risk Management Platforms keep organizations more secure against both today’s and tomorrow’s threats. They provide more bang for buck, with AI-enabled automation getting more impactful results while requiring fewer resources to operate.
| Dimension | Human Risk Management (HRM) | Security awareness training |
|---|---|---|
| Primary objective |
|
|
| Core KPI / Metrics |
|
|
| Training approach |
|
|
| Personalization |
|
|
| Phishing simulations |
|
|
| Threat intelligence |
|
|
| SOC & security operations |
|
|
| Automation & AI |
|
|
| Culture impact |
|
|
| Compliance & governance |
|
|
| Insurance outcomes |
|
|
| Handling repeat clickers |
|
|
| Scope beyond phishing |
|
|
| Technology alignment |
|
|
| Outcomes |
|
|
10 key elements and advantages of HRM include:
- Compliance as a function of risk reduction: HRM measurably and demonstrably reduces risk with behavioral interventions and realtime alerts while delivering ongoing education.
- Outcome-Driven Metrics (ODMs): HRM emphasizes outcome-driven metrics that showcase actual behavior changes, proving that risk is being minimized over time. These ODMs provide security teams and leadership clear evidence of improved employee behavior that safeguards the company.
- Clear Communication of Value: The value of HRM programs can be easily communicated through ODMs, making it easier to demonstrate ROI to stakeholders and decision-makers.
- Advanced, Targeted Approach: HRM leverages AI and automation to create personalized, targeted risk management programs, replacing the “one-size-fits-all” nature of traditional security awareness training.
- Real-Time Detection and Nudge Alerts: Speed is essential. By monitoring activities like email use, data storage, access management, web browsing, and patching practices, HRM systems can trigger nudge alerts to correct risky behaviors before they result in a security incident.
- Human Threat Intelligence for Early Breach Detection: HRM incorporates human threat intelligence into the security stack, enabling early detection and response to threats like phishing and social engineering.
- Accelerated Incident Response: The ability to identify and mitigate risks before they escalate into breaches drastically reduces the potential damage and cost.
- Regulatory Compliance and GRC: With new regulations such as the SEC disclosure law in N America, and NIS2 and DORA in Europe, HRM is far better suited to help the C-suite manage their personal liability alongside governance, risk, and compliance (GRC) requirements. The HRM model provides demonstrable proof of security efforts, which is essential for regulatory reporting.
- Facilitates Cyber Insurance: Obtaining cyber insurance with favorable premiums is increasingly difficult due to stricter compliance requirements. The HRM model’s ability to reduce risk and provide verifiable metrics makes it easier to qualify for cyber insurance and secure better rates.
- Builds culture: Continuous learning and engagement embeds security into organizational culture with measurable participation and progress.
By adopting HRM, security leaders can not only improve the security posture of their organization but also effectively communicate the value of their efforts, reduce risks in real-time, and stay ahead of evolving compliance demands. The old security awareness training model is no longer sufficient in today’s dynamic threat landscape, while HRM offers a forward-thinking, comprehensive solution.
To know if your risk is actually going down, an HRM platform establishes hard numbers around:
- Key risky behaviors
- Risk posture
- Baselines for risky behaviors and risk posture
- HRM-driven changes in behavior from baseline
- HRM-driven risk reduction via improved behaviors
- Business impact of HRM, e.g. reduced costs and operational downtime

Human risk management vs. HR risk vs. insider risk management: which one do you need?
Ask three people in your organization who owns employee risk and you will get three different answers. All three will be partly right. The confusion is fair enough. Every one of these disciplines carries the word risk, and every one of them concerns employees. But they sit with different teams, run on different signals, and get bought for different reasons. Human risk management is the cybersecurity one: it measures and reduces the security risk created by everyday employee behavior.
| Dimension | Human risk management | HR / people risk | Insider risk management |
|---|---|---|---|
| What it manages | Security risk created by everyday employee behavior | Employment risk: conduct, policy, workforce compliance | Misuse of authorized access, malicious or negligent |
| Who owns it | CISO and the security awareness lead | HR and People Operations | Security operations and insider threat teams |
| Core signal | Behavioral telemetry: simulation outcomes, real threat reports, security tool events | HR systems, conduct and performance records | Data movement, access anomalies, data loss prevention alerts |
| Typical trigger | A reported phish, a risky click, an unsafe data action | A grievance, an audit obligation, a policy breach | Exfiltration, privilege misuse, anomalous access |
| What success looks like | Measurable behavior change and fewer human-driven incidents | Workforce compliance and reduced employment-risk exposure | Insider incidents detected and contained |
The overlap is real, and it is worth planning for rather than arguing over. Human risk management is what makes insider risk monitoring proportionate, because it tells you which behaviors are habitual and which are genuinely out of character, and it shares training and policy records with HR without turning into an HR system. So if your problem is that your people keep falling for attacks, human risk management is the category to shortlist. The other two solve different problems.
Where should a Human Risk Management program focus first?
Start with your biggest, most expensive risk. Behaviors associated with social engineering and phishing constitute the greatest risk of data breaches, so HRM should start there. Focus on threat reporting because it is the single-greatest risk-reducing behavior.
Done correctly, Human Risk Management aligns the pillars of cybersecurity: people, processes, and technology. In the process, it will produce behavior change results you’d probably never thought possible. Hoxhunt Phishing Trends Report 2026 data shows that: engagement soars by 6X within 6 months; phishing simulation failure rates fall from about 20% to 3.4% over the first year; and real threat detection climbs from 13% to 71%.
This is cultural transformation, painted with numbers.
Most cyber frameworks and guidelines propose that people should be at the heart of cyber strategy. But only with an HRM platform can that actually be done in a meaningful way, with human behavior and threat intelligence actively integrated into the security stack.
But even with the advent of HRM, Security Awareness Managers (SAMs) and CISOs find little guidance for transcending the tick-box security awareness training model to measure human cyber risk, change behavior and build culture.
The HRM model picks up where the legacy security awareness training model stops, at basic cyber literacy. Different approaches are offered by different platforms, but the unifying thread in the emerging HRM model is that behavior change triggers a cascade of steps:
- Shifting left to reduce bad clicks
- Multiplying real threat detection
- Creating cultural transformation
- Reducing human cyber risk across the most risky cyber behaviors
- Augmenting the SOC
These same principles for managing human risk around phishing and social engineering can then be deployed across the gamut of risky behaviors.
Which HRM metrics matter?
- Training engagement rate: The percentage of employees who actively participate in security training activities, such as phishing simulations or microlearning modules. This metric reflects overall program adoption and cultural buy-in.
- Phishing simulation reporting rate: The percentage of simulated phishing emails that employees correctly identify and report to the security team using the designated reporting process. A higher rate indicates stronger detection and reporting habits.
- Phishing simulation failure rate: The percentage of simulated phishing emails that employees interact with (e.g., clicking a malicious link or opening an attachment) instead of reporting. This measures susceptibility to social engineering.
- Resilience rate: A composite score calculated by dividing the phishing simulation reporting rate by the failure rate. It measures how effectively your workforce detects and reports phishing attempts relative to how often they fall for them.
- Phishing simulation dwell time: The average amount of time it takes for an employee to report a phishing simulation after it lands in their inbox. Shorter dwell times indicate faster threat recognition and response.
- Real threat detection rate: The percentage of actual, non-simulated phishing or malicious messages that employees identify and report. This is a direct measure of real-world vigilance.
- Real threat detection dwell time: The average time it takes for employees to report genuine phishing or malicious messages after they are received. Faster reporting improves the organization’s ability to mitigate threats before they cause harm.
How do we implement HRM step‑by‑step? (CISO playbook)
Human Risk Management begins with managing your greatest risk: social engineering and phishing. Two sides of the same coin, social engineering and phishing include spear phishing, BEC, ransomware, malware, credential harvesting, high volume campaigns, AitM, extortion, romance scams, deep fakes, vishing, smishing, and all other attacks targeted at people.
Social engineering self-defense skills are developed with a training platform built on:
- Behavior - Threat reporting
- Gamification - A design approach based on behavioral science
- Engagement - Highly motivated people keep themselves and colleagues safe
- Meaningful metrics - Measure and manage the behaviors that actually matter, starting with threat reporting
- Automation - Let AI do the heavy operational lifting
- Personalization - Customize training to individual needs and backgrounds
- Adaptive learning - Auto-adjust content and difficulty to user skill level
Security training evolves into Human Risk Management when each employee is equipped with the skills and tools to recognize and report social engineering attacks as naturally as swatting mosquitoes; and the security team has the infrastructure to leverage that threat intelligence for accelerated incident response.
HRM best practices checklist
- Focus on behavior: Make threat reporting your #1 security behavior. Measure success by rising simulated and real phishing reports.
- Choose the right platform: Ensure integration, automation, cultural fit, measurable outcomes, and strong engagement rates.
- Secure executive buy-in: Position HRM as business risk reduction. Use outcome-driven metrics to win C-suite support.
- Build cross-functional bridges: Engage HR, Comms, Marketing, and Sales to amplify your message and create internal champions.
- Break the awareness silo: Connect human threat intel directly into your SOC for real-time incident response.
- Reward, don’t punish: Use gamification, positive reinforcement, and psychological safety to drive participation.
- Measure the metrics that matter: Track real threat detection rates, dwell times, and other ODMs to prove risk reduction.
- Keep training short & frequent: Deliver realistic, engaging micro-learning moments regularly to reinforce skills.
- Target high-risk users: Apply adaptive, risk-based interventions to reform repeat clickers and reduce concentrated risk.
- Integrate with the SOC: Automate categorization and escalation of threat reports for faster, smarter responses.
- Create a feedback loop: Turn real-world attacks into training simulations to keep pace with evolving threats.
- Customize content: Tailor learning to roles, skills, and behaviors using AI-driven personalization.
- Pilot, then scale: Run a proof of concept, benchmark results, and roll out broadly once impact is proven.
- Expand beyond phishing: Apply HRM principles to MFA, data handling, and other risky behaviors.
Step 0: Focus on behavior
Step zero of the Human Risk Management playbook is to focus on behavior, not security awareness. The most impactful cyber behavior is threat reporting because it removes the threat from the system and accelerates incident response. There’s no better proof of a security training program’s effectiveness than a rise in simulated and real phishing reports.
By focusing on the single most important behavior to cybersecurity, you will achieve outsized security ROI.

Fortune 500 energy company, AES won a prestigious CSO50 Award for their gamified security awareness engagement program, which deliberately scrapped the security awareness training model for the gamified security behavior change model. Their results are aspirational. Monster Energy took the same behavior-first path to a CSO Award of their own.
Step 0.5: Select the right platform
Managing a Human Risk Management program entirely in-house takes tremendous resources, starting with the security behavior change operations.
There are several options out there to help you, and our comparison of the best human risk management software lays them out side by side. Find the right tool for the job.
Some considerations when making your cyber training software decision are:
- Will the platform integrate into my environment?
- Is it engaging? What are their engagement rates?
- Does it have good reviews from admins and end users?
- Is it really automated? Sometimes, claims about automation aren’t grounded in fact.
- What measurable outcomes around behavior and risk management are offered?
- Does it do what I need it to do today (e.g. compliance), and will it do what I want to do later on, i.e. reduce risk across multiple core behaviors?
- Does training and user experience align with our cultural values, e.g. reward-based and uplifting vs. punitive and terrifying?
- Is there automatic report generation?
- Are there powerful risk dashboards?
- Is the platform dynamic with the changing threat landscape?
- Will the platform automate the heavy operational lifting?
- Is there a dedicated CS team to get the program moving and keep it on track?
You can find free objective resources for reviewing vendor options on G2 or Gartner Peer Review Insights, where you’ll find that Hoxhunt tops the list, alongside our own rundown of the best security awareness training.
Forrester published its first Human Risk Management Wave in Q3 2024, and Gartner covers the category under its own name, Security Behavior and Culture Programs. Frost & Sullivan awarded Hoxhunt Competitive Strategy Leadership Recognition: The Human Risk Management Industry Excellence in Best Practices.
Also consider soliciting a security consultant such as:
Step 1: Secure executive buy-in
Rolling out a new security training program should be looked at as an exercise in change management. Success will pivot on leadership buy-in. Not only do you need leadership to support your program as role models, you need their approval for the right tools, resources, and budget.
Start by talking the C-suite’s language: business risk. Provide outcome driven metrics that demonstrate the value of the program in terms of behavior change and its impact on reduction of cyber risks and costs.
More and more enterprises have a board seat reserved for a security representative. Some, such as TomTom, even give the CISO a seat on the Board. It’s crucial to establish influence and buy-in to HRM at the very top.
What does buy-in look like? At AES, top performers in security training got a quarterly bonus as part of an incentive model for building their security culture.
Step 2: Build bridges throughout the organization
Form a cross-functional, interdepartmental cyber advisory group. Find influential members of different teams who you can ultimately count on to inform you about their needs and challenges, and become champions of your training program.
Make an effort to reach out beyond IT and connect with people whose job involves communicating corporate messages and programs across the org. Talk to HR, Communications, Marketing, and Sales. These people are trained in communicating vital information to large audiences persuasively.
Get them talking about cyber so much that it becomes a water cooler topic.
Step 3: Break the awareness silo
HRM ultimately dissolves the silo around security awareness to connect human threat intelligence to the security stack. Start doing that with your awareness program. Training touches multiple points of the security function. It should therefore involve representatives across relevant security functions to assist with program management.
Security Awareness Managers can sometimes be left isolated and unsupported, which will limit the effectiveness of the training. HRM connects the fruits of their labor to the SOC. Working together, you can ensure the results of the behavior change program, human threat intelligence, is plugged into the security stack and put to good use. As Victorinox might say, HRM is a Swiss Army Knife where security awareness training is a dull spoon.
Step 4: Reward, don’t punish, and create a culture of ‘Yes!’
CISOs aren’t always as popular as they should be. They sometimes don’t feel included at the proverbial water cooler, and feel uninvited to the C-Suite’s grownup table.
Your training program is the key to unlocking the door to the Room Where It Happens.
Good training positions the conversation you want to have across the organization about cybersecurity as a vitally important topic. You can even make cyber fun and cool. If your cyber training is built on psychological safety, people will be encouraged to reach out to security for help and guidance.
Think of it as transforming the security team’s image from Dr. No to Dr. How. The world’s leading software review site, G2, selected Hoxhunt for its positive psychology approach with gamification, and reported that they’d “seen the light” with the uplifting approach to people and culture.
Step 5: Starting with your biggest risk, measure ODMs that matter
Measurement is the bedrock of Human Risk Management. The defining characteristic of HRM is outcome driven metrics (ODM), and there’s no better ODM than real threat detection. Connecting the behavior change in the simulated and real environments, namely threat detection, demonstrates that risk is being reduced at its greatest source, and breaches are being mitigated and prevented.
So start by building your human risk management program around threat reporting behavior. Reward those good clicks in-platform with a digital high five.
Phishing doesn’t stop at training, so neither should your program’s metrics. It’s crucial to track how well, how fast, and how often people are recognizing and reporting real threats. A surge in real threat detection is the best proof that phishing training is making an impact. Having a training platform whose reporting button can be used on real and simulated phishing attacks is a huge help.
4 Essential Outcome-Driven Metrics (ODMs) in Human Risk Management
1. Phishing Simulation Reporting Rate
- Formula: (Number of simulated phishing emails correctly reported ÷ Total simulated phishing emails delivered) × 100
- Why it matters: Measures how often employees recognize and report simulated threats, indicating detection skill and proactive behavior.
2. Phishing Simulation Dwell Time
- Formula: Average time from simulated phishing email delivery → employee report submission
- Why it matters: Shorter dwell times reduce the window for an attacker to exploit a click before the SOC can respond.
3. Real Threat Detection Rate
- Formula: (Number of real phishing/malicious messages reported ÷ Total real phishing/malicious messages received) × 100
- Why it matters: Tracks real-world detection capability beyond simulations, proving HRM’s impact in live environments.
4. Real Threat Detection Dwell Time
- Formula: Average time from real threat delivery → employee report submission
- Why it matters: Measures the speed of real incident escalation, directly affecting breach prevention and SOC efficiency.
Step 6: Reporting
A good platform will generate reports on the above metrics, and more, that you can show to leadership to communicate the value of your program and its effectiveness. Risk dashboards help with this, as do auto-generated reports around relevant metrics such as phishing simulation reporting and failure rates, engagement rates, threat detection and mitigation, and dwell time.

Step 7: Target behavior-based engagement, not failure rate
The HRM program is built on engagement. If people aren’t learning, then they aren’t improving. In a behavior-based program, the best way to achieve engagement is to reward good behavior and gently coach away bad behavior. The Hoxhunt platform does this via gamification, with in-platform rewards like stars, badges, and leader boards.
Engagement with an awareness training tool is less outcome-based and more opaque, as everything other than failing a phishing simulation is tacitly accepted as a success.
Punishment-based training limits training experiences to only those who click on a simulated phish. Most companies have engagement rates between 5% to 20% with a traditional quarterly security awareness training program. Giving training only to that small portion of phishing simulation failures ignores the vast majority who passed on it. And the negativity associated with cyber training sours people on the whole topic.
Encourage people to be courageous and act. You want an open dialogue between security and the rest of the organization. If someone clicked, the faster they report it then the faster you can mitigate the damage.
Docusign said they selected Hoxhunt for satisfying several behavioral science criteria, including frequency of reward-based training. And Avanade added that they wished for a program that was designed to meet people where they’re at, in order to take them where they need to go.
Exponentially fewer data points are available with an unengaged employee population. In a hypothetical 10,000-person company, a security awareness training tool that produces a 10% engagement rate with 4 simulations per year, compared to a behavior change program with a 50% engagement rate on 36 simulations per year, breaks down to:

Security awareness training: 4,000 data points, confined to a small cohort
Behavior Change: 180,000 data points, representing a statistically significant cohort
Those counts come from the Hoxhunt Phishing Trends Report 2026, measured across a 10,000-person organization.
Understanding what makes your people tick (and click), and turning that around starts with measuring the behaviors you want to improve.
Step 8: Make training frequent, short, and varied
A yearly or quarterly video won’t cut it. A massive library of dry, uninteresting content won’t move the needle. So stop thinking about quantity, and focus on quality of engagement.
Research like that of Stanford’s BJ Fogg shows that behavior change happens with engagement with frequently repeated practice. Recognizing and reporting phishing simulations takes 30-60 seconds, and can be followed by an awareness micro-training moment. Threat reporting is a behavior that can be conditioned with the repeated, realistic practice of spotting telltales of social engineering attacks and reporting them with a simple and rewarding process.
If people aren’t engaged and actively reporting threats, they aren’t learning. So begin conditioning cyber-positive behavior with carrots, not sticks.
Step 9: Risk-based, targeted interventions
Research by Cyentia has shown that 4/5 of cyber events are caused by just 4% of employees, mostly from repeat clickers of malicious links. Qualcomm identified their own subset of repeat offenders and enrolled those 1,000 employees in an adaptive phishing training program. The “Risky 1K’s” results in periodic benchmark tests were compared against the rest of the 50,000-employee company.
A few people can cause the most problems
- 80% of phishing breaches are caused by 4% of users
- 92% of malware events are caused by 3% of users
- 1% of users will average an incident every other week
Within months, the Risky 1K were reformed. They graduated from phishing prisons to the head of the class, and outperformed the rest of the company so significantly that the security team secured approval for an org-wide Hoxhunt roll-out that has since improved phishing simulation failure rates globally by 6X.

These results earned a prestigious CSO50 Award from Foundry.
Step 10: Connect your training output to your SOC input
Human threat intelligence is a terrible thing to waste.
A good behavior change program will result in a 10X increase in real threat reports to your threat feed. Today, as more and more sophisticated threats bypass email filters, that human threat intelligence is a competitive advantage when integrated into the security stack. It’s the army behind the moat behind the castle walls, who also actively report spies who try to enter and reinforce the castle walls with the cannon balls and arrows they collect from the enemy; it’s another active security layer behind the technical firewall.
Find a platform that will auto-categorize the threat reports and escalate the prioritized incidents for response. This will accelerate SOC response and augment the quality of their work.
Step 11: Create a feedback loop between training content and the threat feed
It’s important to stay at the cutting edge of the constantly-evolving threat landscape. Transform the latest phishing attacks into valuable learning experiences by reformatting them into hyper-realistic phishing simulations, which is where the right phishing simulation software earns its keep.
Step 12: Customizable content
Training must be relevant to the user’s background, job role, and skill level as they change over time. Find a training platform that automatically adapts training from its library, via AI, to the user’s needs. From there, you can further use AI in the platform to create targeted content that suits your goals.
Step 13: Execute a Proof of Concept trial
Perform a cyber challenge. Put different segments of your employee user base on different training programs, and compare their results with periodic benchmark tests. Let the results speak for themselves.
The transformative results of Qualcomm’s “Worst-to-First Employee Phishing Performance” precipitated an org-wide rollout of Hoxhunt that measurably reduced risk by orders of magnitude. AES, Avanade, TomTom, Bird&Bird, DocuSign, and Victorinox are just a few examples of enterprises who started with a POC that led to a general rollout. It helps to set the clock up front: per the Hoxhunt Phishing Trends Report 2026, behavior change is measurable within three months, and cultural change follows by six.
Step 14: Ace the roll-out
Every preceding step has positioned you for a successful rollout. Having leadership buy-in and a stable of cybersecurity champions supporting you, launch the full program with the platform’s dedicated customer success team. You’ll likely be sending out a series of communications that will alert the organization of your new Human Risk Management program. This will officially kick off with a training email that walks users through the process of using the reporting button integrated into the email client. A good platform will be interactive even in the onboarding communications. It should feel like a video game: easy enough that the user feels a sense of success and accomplishment with the first training experience to crave more.
Step 15: Now measure, manage, and mitigate the other risky behaviors
The principles of an HRM approach to social engineering can be applied to a broad range of human behaviors. Having established a security culture with your security awareness and phishing training program, the security team can now address the other threats that the HRM platform alerts them to.
The platform should do the heavy lifting. When a user doesn’t properly use MFA, or securely browse the web, or share sensitive data, then the platform can alert both the user and the admin and trigger a behavioral nudge in real time. It’s up to the security team to decide the most prudent course of action upon prevalent trends.
Results: humans are your greatest resource
Imagine if everyone from the board room to the mail room were so excited about cybersecurity they actually asked you for more training.
Imagine if your engagement rate were to soar from 10-20% to over 60%.
Imagine if your engagement was built on the critical behavior of reporting both simulated and real phishing attacks.
Imagine if people clicked 6 times less on phishing emails.
Imagine if 2/3 of your workforce were actively reporting real threats.
With a good HRM platform, this can all be achieved, not just imagined.

The above improvement is dramatic, and it’s the product of:
A) An effective HRM platform
B) A dedicated Customer Success team that gets the program on track, and ensures it stays on track.
These results represent the progress of 2 million users who’ve onboarded with the help of a Hoxhunt CS team. Across that population the Hoxhunt Phishing Trends Report 2026 finds that two thirds of employees report a real threat within their first year. The baseline engagement, failure, and threat reporting rates with old-school security awareness training tools vary between company and program. We’ve seen that behavior-based engagement is around 7%, with 20% failure rates, and 80%+ unengaged populations. Most companies, even highly mature ones like AES, report 10% engagement rates with standard tools.
But during onboarding with a security behavior change program, something magical happens: a phase change occurs. Behavior-based engagement soars by over 6x. Failure rates are cut in half. And that’s just with the onboarding.
Once the program is on track, the platform continues the magic.
Phishing simulations are sent every 10 days. Even though they are designed to get harder as the user’s skill level improves, failure rates continue to drop while threat reporting rates continue to climb. Users stay engaged for years on end as the difficulty level of the training remains just hard enough to give people a sense of accomplishment with every threat report. And those gains are locked in by the platform’s Instant Feedback feature, which rewards real threat reports with realtime feedback so people know immediately the impact they’ve made on their org’s security.

People stay engaged for years on end. Their behavior change is sustained. Employees become the solution to the very problem of human risk.
4Xdrop in failure rates at Monster Energy, from 16 to 18% with legacy security awareness training to 4%. United StatesRead the Monster Energy case study →
85%phishing simulation reporting rate at Swisscom, with failure rates down from 15% to below 2%. EuropeRead the Swisscom case study →
What does a mature human risk management program look like?
Maturity here is a curve, not a certificate. You do not reach it in a quarter, and no vendor hands it to you at signature. The milestones below come from the Hoxhunt Phishing Trends Report 2026, which follows the same cohorts over time, so they describe what a working program actually does month by month.
| Stage | When | What the data shows | The metric that proves it |
|---|---|---|---|
| Baseline | Month 0 | Simulation failure rate around 20%, real-threat detection near 13% | Failure rate |
| First movement | Months 1 to 3 | Behavior change becomes measurable inside the first quarter | Training engagement rate |
| Behavior change | Months 3 to 6 | Real-threat detection reaches roughly half of the curve; cultural change becomes visible by month six | Reporting rate |
| Culture | Months 6 to 12 | Failure rate falls toward 3.4% across the first year | Failure rate and repeat-clicker concentration |
| Mature | Month 12 and beyond | Real-threat detection around 71%; reporting holds above 20% | Real-threat reporting share |
The bottom line
If you only watch one number, watch the reporting rate. A sustained rate above 20% means behavior has genuinely changed and reporting has become the norm, where awareness-only programs tend to plateau near 10%. And if that number has been flat for a year, be honest about what that tells you. The program is running. It is not maturing.
How can CISOs handle repeat clickers without creating a blame culture?
Your repeat clickers, meaning employees who consistently fail phishing simulations, should be met with adaptive, supportive training, not punishment. Generic, one-size-fits-all remediation often fails. Instead, tailor simulations and microlearning to the specific phish they missed, escalate difficulty over time, and reinforce reporting habits to turn high-risk users into active security defenders. Read our full guide to dealing with phishing repeat offenders.
Key strategies for reducing repeat phishing clicks:
- Analyze patterns: Identify phishing types, risk factors, and roles most prone to repeated clicks
- Adapt difficulty: Increase simulation complexity gradually, based on individual performance
- Deliver just-in-time training: Provide short, scenario-based microlearning after each failure
- Personalize content: Target blind spots with relevant phishing templates (e.g., QR codes, credential harvest)
- Encourage reporting: Reward rapid incident reporting to build security-conscious culture
- Avoid punitive measures: Use empathy and guidance to maintain engagement and trust
How should HRM integrate with the SOC and security operations?
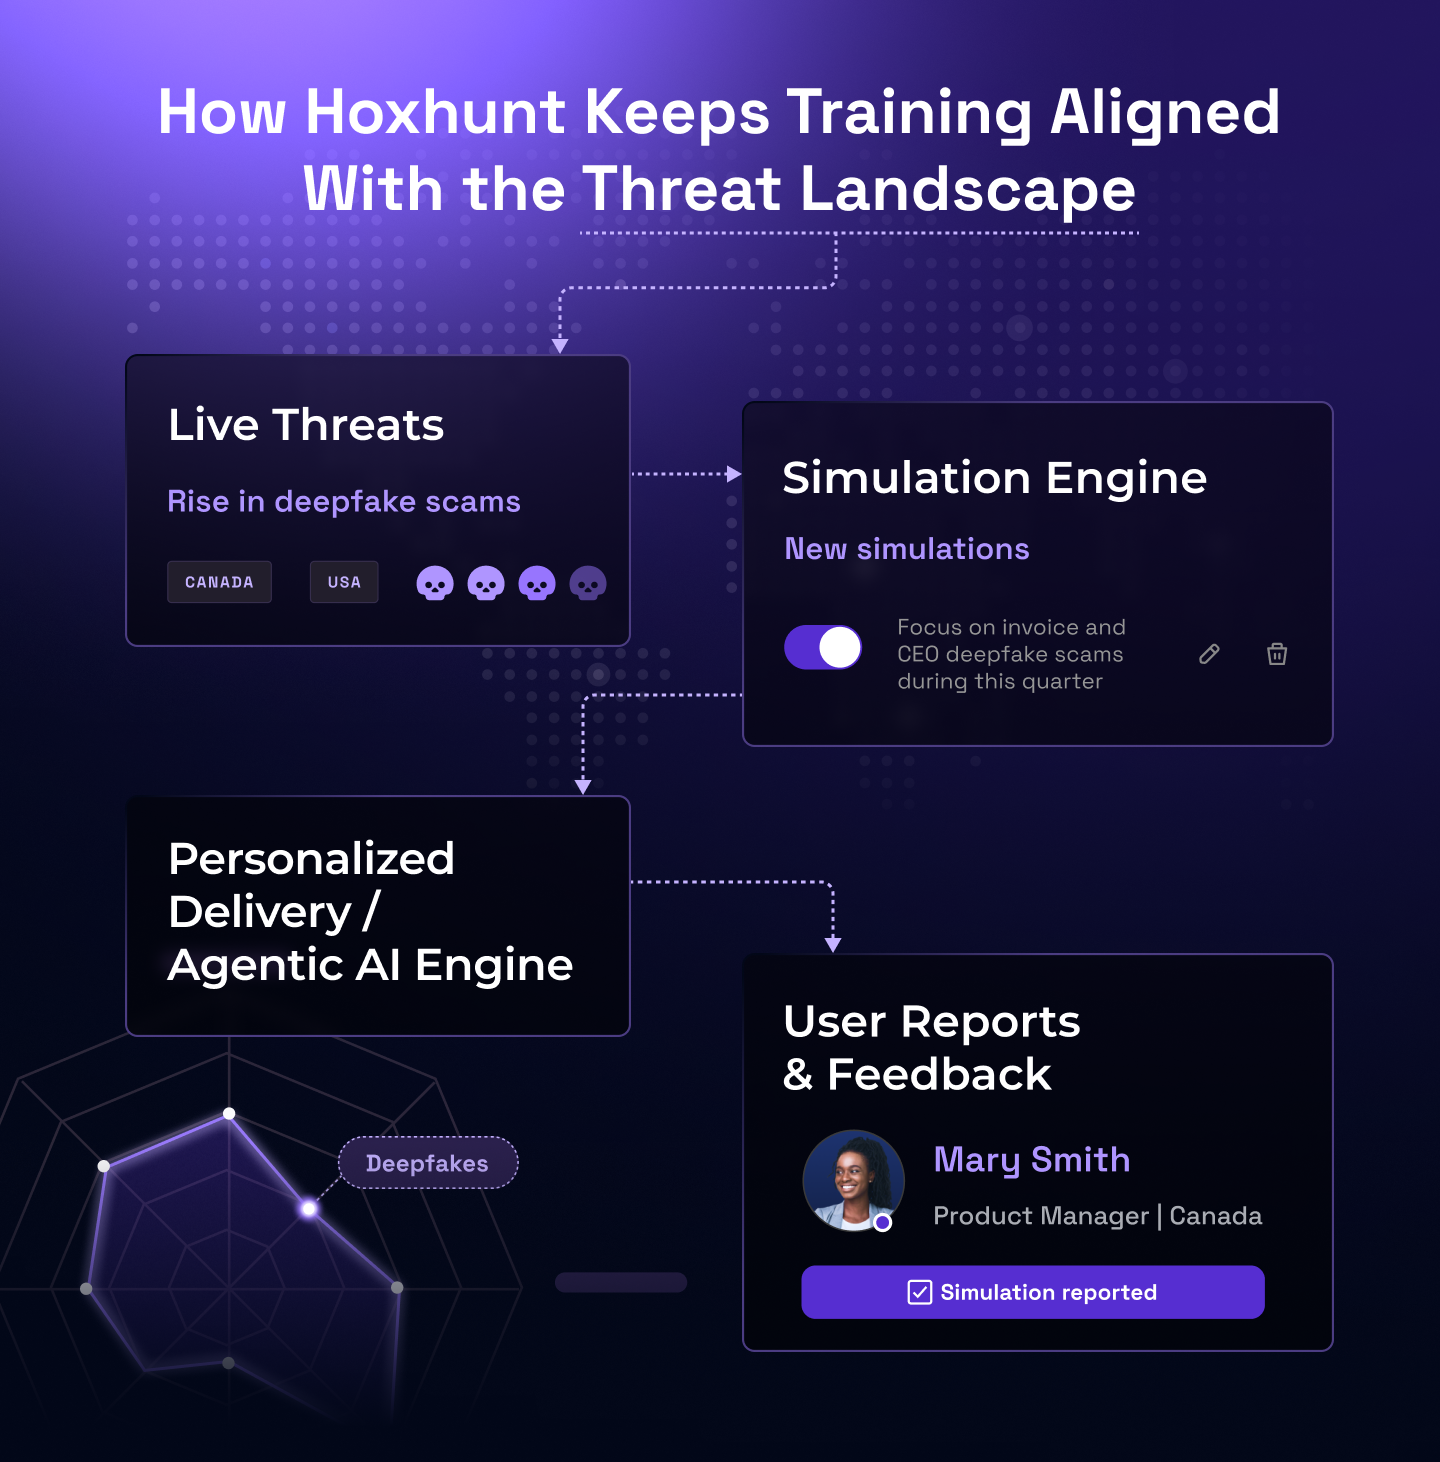
Human Risk Management integrates with the SOC by turning user-reported threats into actionable intelligence. Hoxhunt, for example, feeds real phishing reports into the security stack, auto-categorize incidents, and feeds that data back into hyper-realistic simulations.
Closing the loop between people and SOC workflows
When employees report suspicious emails, those alerts shouldn’t vanish into a helpdesk queue. HRM platforms can route them directly into SOC tools, enabling analysts to triage incidents in real time. This human threat intelligence becomes a valuable extension of your technical defenses. Speed is what makes it useful: in the Hoxhunt Phishing Trends Report 2026, the fastest 5% of employees report a real threat in about 39 seconds, and median dwell time drops by roughly a third.
Automation is key to keeping the SOC efficient. AI can categorize and prioritize reported threats, whether it’s a QR code scam, a credential harvest attempt, or a business email compromise, so analysts spend less time sorting and more time responding.
The real power comes from feeding those confirmed threats back into training. Hoxhunt uses real attack data from its customers’ environments to create hyper-realistic phishing simulations. This ensures employees are training on the exact tactics threat actors are using, not outdated scenarios from a generic template library.
Below you can see the Live Threats → Simulation Engine → User Reports loop.
What reporting does leadership and the board expect on human risk?
Your board expects clear, business-focused reporting on human risk, linking security behaviors to measurable reductions in cyber risk, incident costs, and regulatory exposure. Effective HRM reporting goes beyond click rates, providing outcome-driven metrics that prove resilience gains and align with compliance, governance, and strategic priorities.
Turning security metrics into business language
Board members and executives aren’t looking for raw phishing click rates. They want to understand risk in business terms. This means framing HRM results around how improved employee behavior reduces the likelihood and impact of data breaches, insider threats, and costly security incidents.
Outcome-driven metrics (ODMs) like phishing simulation reporting rates, real threat detection dwell time, and resilience rates show whether behavior change is actually happening. When these are tied to cost avoidance or incident response improvements, they become powerful indicators of ROI.
Regulatory alignment is also a growing priority. Many boards now want to see how HRM supports compliance with frameworks like ISO 27001, NIS2, or SEC cyber disclosure rules. Demonstrating proactive risk governance can also improve cyber insurance negotiations.
Best practice is to present these insights visually, using risk dashboards that map trends over time, highlight high-risk behaviors, and benchmark performance against industry peers. This makes human risk reporting a strategic conversation, not just a technical update.
Here’s what reporting looks like in Hoxhunt...
Why Hoxhunt is the trusted choice for Human Risk Management
Hoxhunt is recognized by Frost & Sullivan, Gartner Peer Insights, and G2 as a top performer in human risk reduction, with proven results across 4 million+ users.
Why? Because our platform is built from the ground up to deliver outcome-driven metrics, adaptive learning, and real-time threat intelligence that transforms employee behavior.
According to Frost & Sullivan’s Customer Transformation Journeys Report, Hoxhunt clients have achieved:
- Up to 225% increases in phishing reporting rates
- Over 3x reduction in phishing click rates
- Significant gains in incident visibility, dwell time reduction, and SOC efficiency
What sets Hoxhunt apart
Adaptive training at the individual level: Every simulation, microlearning, and nudge is personalized based on a user’s role, behavior patterns, and demonstrated risk factors. We escalate difficulty intelligently, meeting users at their point of failure to build resilience without creating training fatigue.
Real threat data powering training: Our simulations are built from live, real-world phishing and social engineering attacks detected in our customers’ environments. This ensures every training scenario reflects the latest tactics, techniques, and procedures used by actual threat actors.
Seamless SOC integration: Hoxhunt feeds verified, user-reported threats directly into your SOC and security stack, auto-categorizing incidents and closing the loop between reporting, analysis, and training. This dramatically reduces dwell time and improves incident response.
Behavioral analytics for measurable ROI: Our platform tracks key human risk metrics, namely resilience rate, dwell time, and reporting accuracy, so you can prove risk reduction to leadership, regulators, and insurers. Risk dashboards give instant visibility into organization-wide security posture.
Culture-building at scale: Gamification, positive reinforcement, and role-based recognition turn security into an engaging, empowering experience. Users stay motivated, report threats faster, and become active participants in defending your organization.
Proven at enterprise scale: From Qualcomm’s “Risky 1K” transformation to AES’s 6x engagement boost, Hoxhunt consistently delivers measurable security culture change for organizations with tens of thousands of users, across industries, geographies, and regulatory environments.
Want to see how Hoxhunt works? You can see what our training looks like below.
Become a Human Risk Management expert
Human Risk Management FAQ
Which compliance, insurance, and governance outcomes improve with HRM?
HRM provides verifiable metrics that demonstrate proactive risk reduction, which is critical when you need to meet frameworks like ISO 27001, NIS2, DORA, and SEC disclosure rules. By reducing incident likelihood, HRM can improve cyber insurance eligibility and lower premiums, while strengthening governance and risk oversight at the board level.
What results can we expect from a mature HRM program?
Organizations often see a 6x increase in engagement, significant drops in phishing simulation failure rates, and major spikes in real-threat reporting. These gains translate into faster incident detection, reduced dwell time, and a stronger security-conscious culture across the workforce.
How do we assess HRM maturity and progress?
Use frameworks like the Human Risk Management Maturity Model or Human Risk Index to track baseline behaviors, risk posture, and measurable improvement over time. Reviewing ODMs such as resilience rate, reporting rates, and dwell time helps confirm whether human cyber risk is trending downward.
Who should lead HRM and how do we gain leadership support?
HRM is most effective when led by a dedicated Human Risk Manager or a Security Awareness Professional with cross-functional influence. Gaining executive sponsorship is essential, so link HRM outcomes to business risk, compliance obligations, and culture change to secure resources and visible leadership buy-in.
Which non-phishing risks can HRM address?
While phishing is often the starting point, HRM can target behaviors like poor MFA adoption, unsafe data sharing, insecure device configuration, and slow patching. Extending HRM across these areas broadens risk reduction and supports a stronger overall security posture.
Sources
IBM Report: Escalating Data Breach Disruption Pushes Costs to New Highs – July 2024
Verizon Data Breach Investigations Report – 2025 Edition
Gartner Top Cybersecurity Trends of 2024 – Hoxhunt – 2024
Comcast Business 2024 Cybersecurity Threat Report - 2024
IBM Cost of a Data Breach Report - 2025 Edition
The State of Phishing 2024 – SlashNext - 2024
World Economic Forum: 95% of Cybersecurity Incidents Due to Human Error - 2024
Hoxhunt vs. KnowBe4 Security Awareness Training – G2 - 2025
Hoxhunt Product Reviews – Gartner Peer Insights - 2025
Hoxhunt Phishing Trends Report – 2026 Edition
The Forrester Wave: Human Risk Management Solutions – Q3 2024
Gartner: Influence and Drive Secure Employee Behaviors – 2026

